Cloud Penetration Testing2026-08-25T07:52:33+00:00

Cloud Penetration Testing

CodeShield delivers CREST-accredited cloud penetration testing to organisations across the UK running workloads in AWS, Azure, and Google Cloud.

Get a FREE penetration test quote today

Crest Member Logo
OSCP Logo
Crest LOGO

CREST-accredited cloud penetration testing

Cloud application penetration testing service

CodeShield delivers CREST-accredited cloud penetration testing to organisations across the UK running workloads in AWS, Azure, and Google Cloud. Cloud breaches rarely come from clever exploits. They come from misconfigurations, over-permissive access, and exposed storage, the everyday gaps that automated scans skim over.

Our specialists combine deep manual testing with configuration benchmarking to find them before an attacker does. No false positives, no fluff. Just clear, prioritised findings and practical remediation advice from a dedicated expert who works with you from scoping through to fixing every issue we find.

Three men laughing looking at a laptop in front of TV
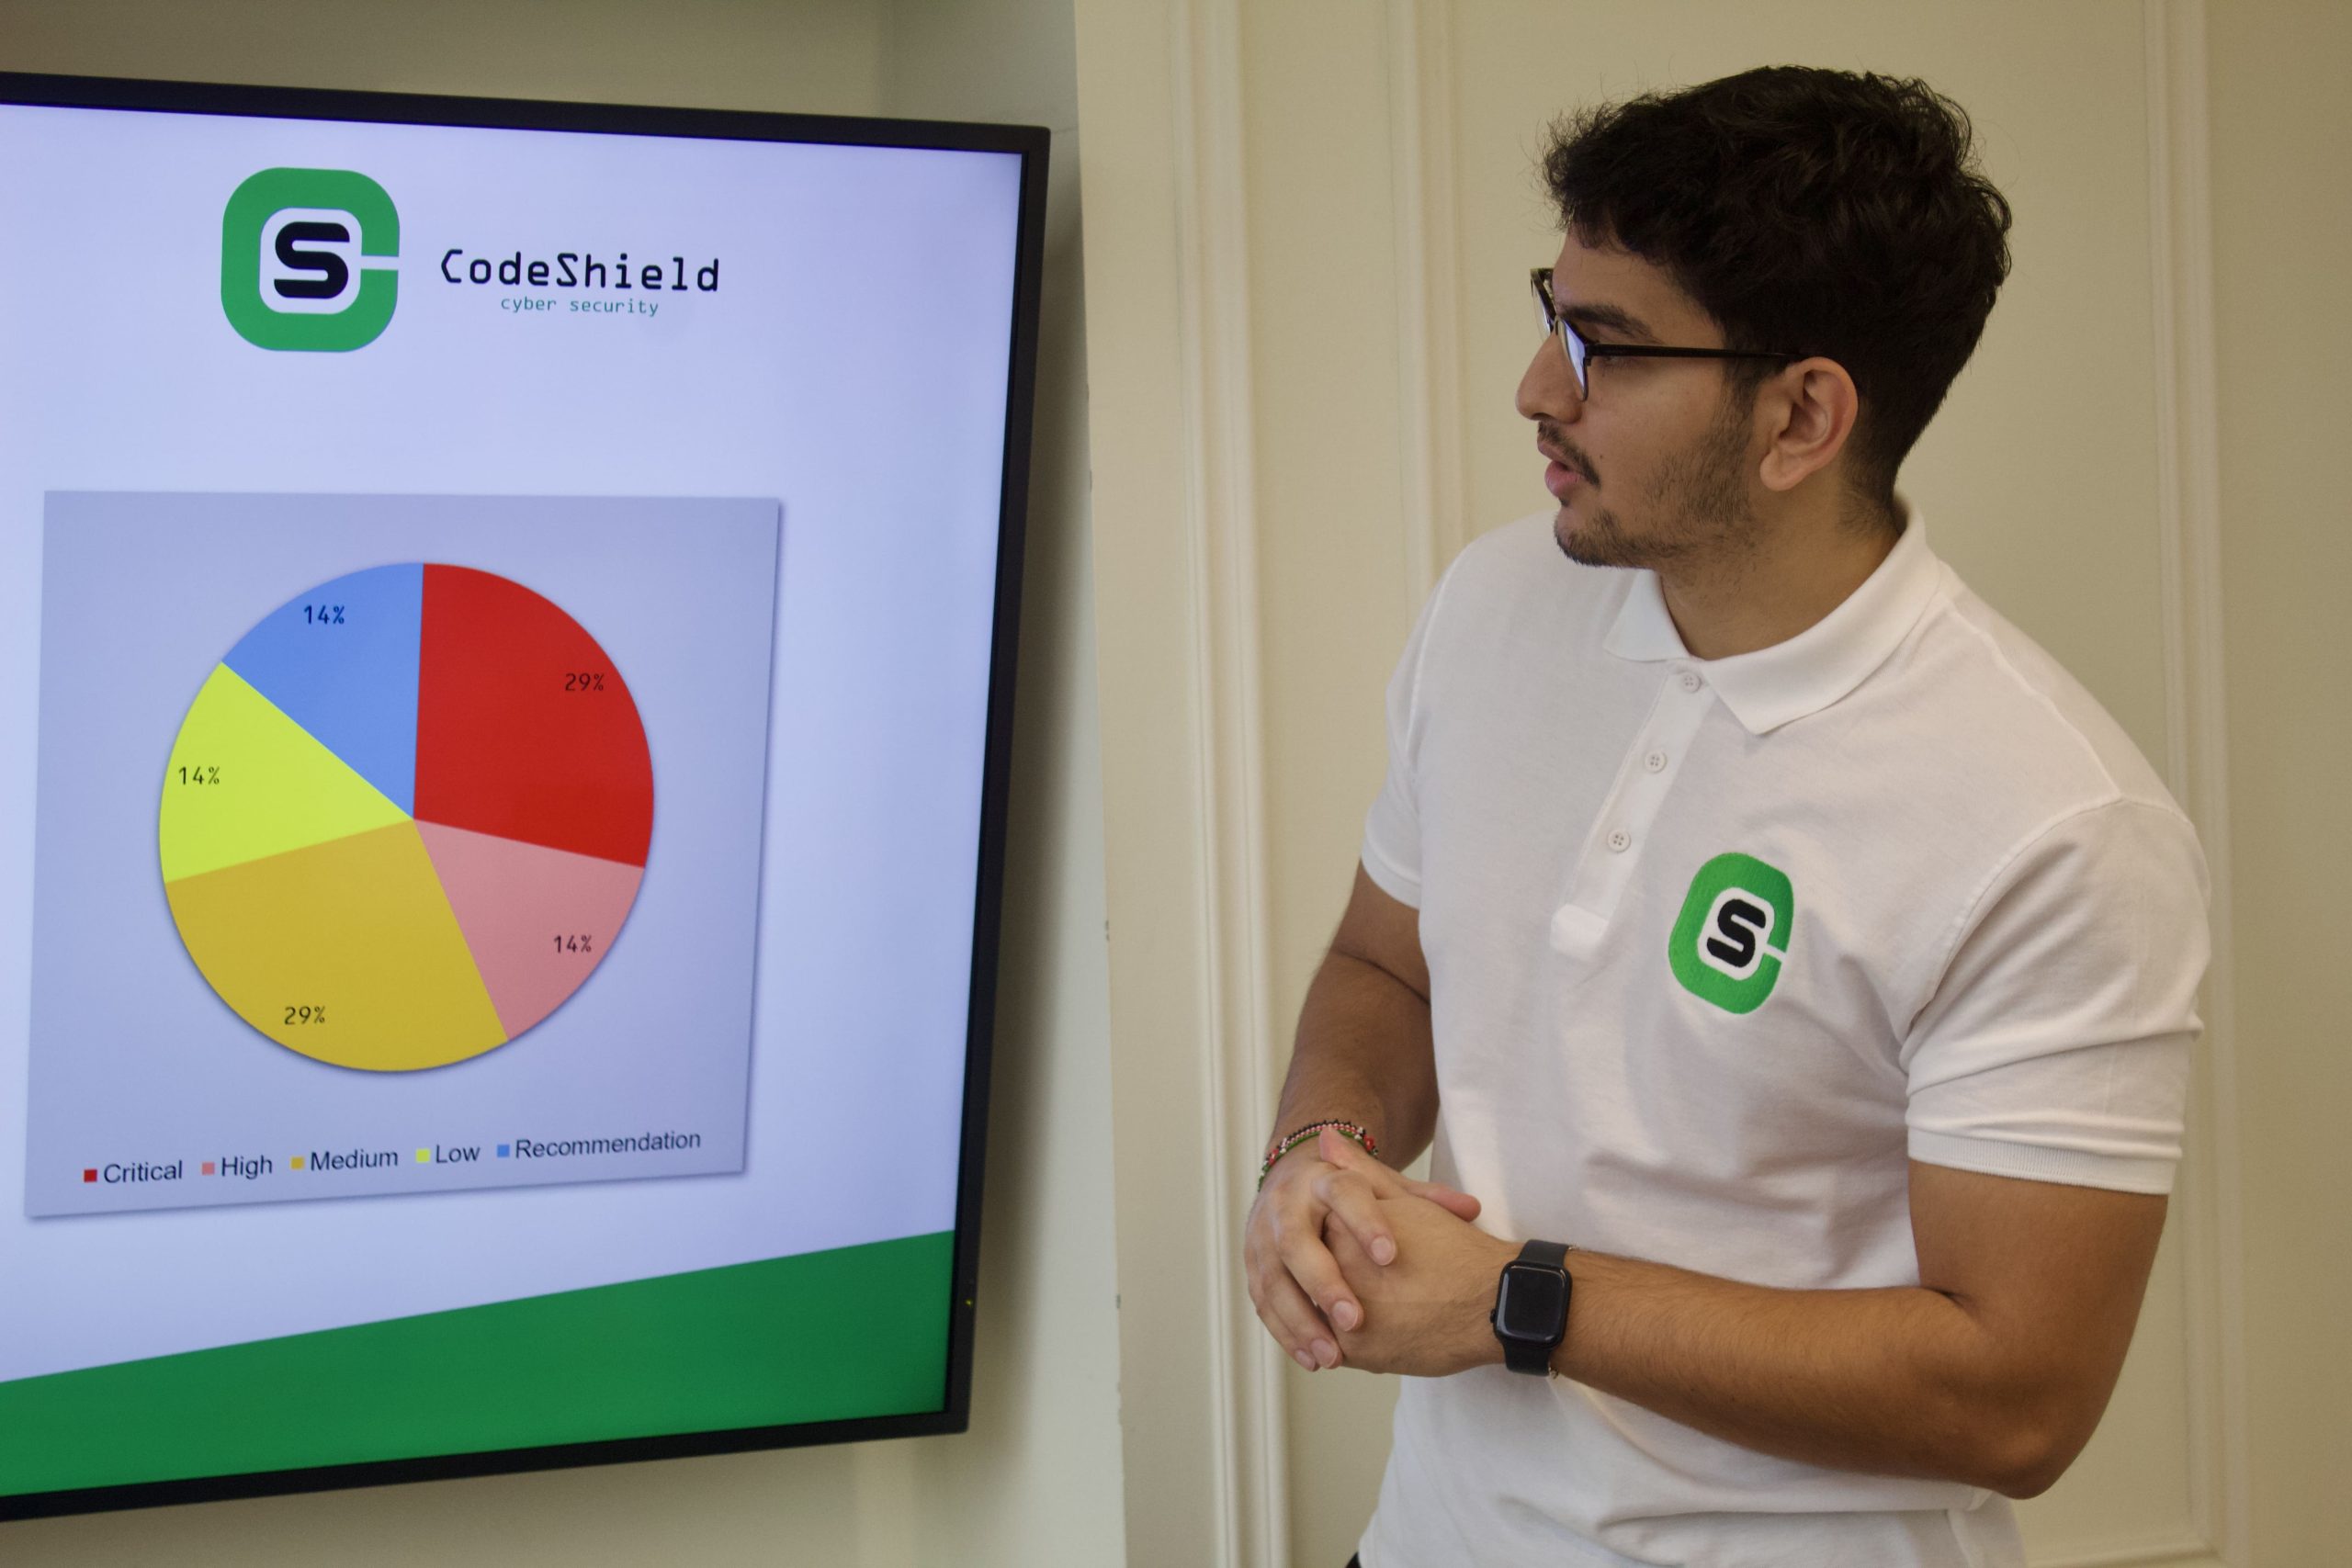
Man with codeshield shirt looking at screen of penetration testing report

What our cloud penetration testing covers

Cloud environments move fast and change constantly, which is exactly why they drift out of a secure state. We test the whole picture, combining CIS benchmarking with hands-on manual testing to find the cloud-specific weaknesses that generic tools miss.

  • Identity and access management (IAM): We test for over-permissive roles, excessive privileges, and weak policies, the misconfigurations that most often let an attacker escalate from a small foothold to full control.

  • Storage and data exposure: We check for publicly exposed and misconfigured storage, including S3 buckets, Azure blobs, and GCP buckets, that could be leaking sensitive data without you knowing.

  • Cloud configuration and CIS benchmarking: We benchmark your environment against CIS best-practice standards, identifying the misconfigurations and insecure defaults that quietly widen your attack surface.

  • APIs and interfaces: We test the APIs and management interfaces that control your cloud for authentication gaps, insecure design, and excessive data exposure.

  • Compute, containers, and serverless: We assess virtual machines, containers, and serverless functions for insecure configurations, unpatched vulnerabilities, and exploitable metadata services.

  • Network and perimeter: We review security groups, networking rules, and exposed endpoints to find the paths into your environment that shouldn’t be open.

Cloud environments move fast and change constantly, which is exactly why they drift out of a secure state. We test the whole picture, combining CIS benchmarking with hands-on manual testing to find the cloud-specific weaknesses that generic tools miss.

WHY TRUST CODESHIELD

Trusted & Independently verified.
Crest Accreditation Logo

“We recently engaged CodeShield to carry out penetration testing for one of our clients, and the service was nothing short of excellent. Both Tom and Dan were extremely knowledgeable and professional throughout the process. Their clear communication and technical expertise made the entire experience smooth and efficient. We look forward to working with them again when the need arises and would highly recommend their services.”

Darren Walsh

“We’ve used a number of CREST assured pen testing companies over the last 10 years, however CodeShield have been the first to exceed my expectations. The team listened to what we wanted, added their own expertise and recommendations and then performed a bespoke test with meaningful, well set out results. The follow-up meetings between our dev team and the testers was well run and respectful. I highly recommend CodeShield and will be engaging them again for our future testing.”

Daren Martin

“We used CodeShield for a security and penetration testing audit for one of our clients. As well as being technically competent and very efficient in carrying out the audit, they were extremely communicative and collaborative throughout the whole process. The result is that we are now very well equipped for the big launch and rolling out the platform to Schools securely.”

Justin Coulston

Client’s we’ve worked with.

CREST accredited penetration testing you can trust

When it comes to security testing, credentials matter. CodeShield is a CREST accredited penetration testing company, holding one of the most respected accreditations in the industry.

CREST accreditation isn’t a badge you buy. It’s independent proof that our methodologies, technical expertise, data handling, and quality processes have been rigorously assessed against internationally recognised standards. For you, it means the testing of your cloud environment is carried out to a benchmark your clients, auditors, and stakeholders already know and trust.

Why CREST accreditation matters for your business

  • Independent assurance: your testing is validated against standards set and monitored by the industry’s leading not-for-profit accreditation body.
  • Procurement-ready: many enterprise customers and public sector frameworks require, or strongly prefer, a CREST accredited provider before they’ll engage.
  • Compliance confidence: CREST accredited testing supports frameworks like ISO 27001, SOC 2, and PCI DSS, giving auditors the credible evidence they’re looking for.
  • Certified people, not just a certified company: our testers hold individual industry certifications from bodies including CREST and Offensive Security, so your project is always in expert hands.

When you choose CodeShield, you’re partnering with a trusted UK security consultancy that combines independent accreditation, technical excellence, and clear guidance to protect your business against real-world threats.

Cloud penetration testing for cloud-reliant businesses

Cloud penetration testing matters most to organisations that run business-critical systems and sensitive data in the cloud, especially those in regulated or security-conscious industries.

If you host applications, data, or infrastructure in AWS, Azure, or Google Cloud, cloud penetration testing should be part of your security programme.

Securing the cloud infrastructure your platform and your customers depend on.
Protecting cloud-hosted payment flows and financial data under FCA and PCI DSS expectations.
Securing patient data in the cloud and supporting NHS DSP Toolkit and compliance requirements.
Protecting cloud-hosted storefronts, customer data, and payment systems.
Testing the cloud platforms that hold high-value personal, claims, and case data.
Validating security during and after migration, when misconfigurations are most likely to creep in.
Three employees looking at each other

Meet your compliance requirements with confidence

Many organisations first come to us because a framework, auditor, or enterprise customer requires independent testing of their cloud environment. We make that requirement straightforward to meet, and turn it into genuine security improvement.

Our cloud penetration testing supports:

  • CIS Benchmarks: testing against the recognised best-practice standard for cloud configuration.

  • ISO 27001: independent testing to evidence your information security controls.

  • SOC 2: assurance for the security criteria your customers and auditors expect.

  • PCI DSS: testing to meet cardholder data security obligations.

  • GDPR: demonstrating that you take the protection of personal data seriously.

You’ll receive a clear, audit-ready report that maps findings to what your framework actually asks for, plus practical remediation advice to close the gaps, not just document them.

WHY CODESHIELD – 20+ YEARS EXPERIENCE

You work with the person doing the testing.

At CodeShield, our UK penetration testing team brings 20+ years of combined expertise delivering practical, results-driven security solutions tailored to your business.

You work directly with a fully-qualified pen tester. You meet them before you pay, so you know who you’re working with.

  • Find & Fix Vulnerabilities: Uncover hidden threats with expert-led testing and gain true confidence in your security.
  • Simplify Compliance: Navigate ISO, PCI DSS, SOC 2 & DSPT with clear, actionable guidance, not just box-ticking.
  • Strengthen Your Defences:  Prioritise real risks and improve your security posture with insights from seasoned professionals.
  • Save Time & Reduce Complexity: We handle the technical details, letting you stay focused on your business.
Man with headset on looking at laptop

TRUSTED UK PENETRATION TESTERS

Contact CodeShield today to get a quote or work with us

At CodeShield, our UK penetration testing team brings 20+ years of combined expertise delivering practical, results-driven security solutions tailored to your business.

Get a FREE penetration test quote today

Crest Member Logo
OSCP Logo
Crest LOGO
Two men looking at a laptop in a meeting room

What makes our cloud penetration testing different

  • CREST accredited, independently assured: Choosing a CREST accredited penetration testing company means your testing is carried out to internationally recognised standards, the assurance your clients, auditors, and stakeholders are looking for.

  • Manual, benchmark-led testing, not just a scan: Automated tools flag the obvious and miss the rest. Our specialists combine CIS benchmarking with deep manual testing to find the IAM flaws, exposed storage, and chained misconfigurations a scanner can’t join together.

  • Genuine cross-platform expertise: We test AWS, Azure, Google Cloud, and hybrid and multi-cloud environments, tailoring each engagement to the platforms and services you actually run.

  • One dedicated expert, start to finish: No handoffs, no account-manager buffer. The specialist who scopes your test runs it and debriefs you personally.

  • Reports people actually act on: Prioritised by risk, written to be understood by technical teams and non-technical stakeholders alike, with clear remediation steps for every finding.

Our Values

Open Mindedness

We believe there’s no single solution to a security challenge. By staying open to new ideas and approaches, our teams find the best outcomes for every unique obstacle we face.

Honesty & Integrity

We believe there’s no single solution to a security challenge. By staying open to new ideas and approaches, our teams find the best outcomes for every unique obstacle we face.

Professionalism

We believe there’s no single solution to a security challenge. By staying open to new ideas and approaches, our teams find the best outcomes for every unique obstacle we face.

Collaboration

We believe there’s no single solution to a security challenge. By staying open to new ideas and approaches, our teams find the best outcomes for every unique obstacle we face.

What’s in your cloud penetration testing report

The report is where a penetration test earns its value. A test is only as useful as the document that comes out of it, and ours are built to be read and acted on, not filed away. Every engagement ends with a clear, structured report that works for your technical team and your senior stakeholders alike.

  • Executive summary: A plain-English overview of what we tested, what we found, and what it means for your business, written so a non-technical reader can understand your risk position in a couple of minutes.

  • Risk-prioritised findings: Every vulnerability and misconfiguration we identify, rated by severity and real-world impact, so you know exactly what to fix first. No noise, no padding, just the issues that matter, in the order they matter.

  • Technical detail and proof of concept: For each finding, a clear explanation of the issue, proof-of-concept evidence showing how it could be exploited, and everything your team needs to reproduce and verify it.

  • Benchmarking against best practice: Where relevant, findings are mapped against CIS benchmarks and cloud provider best practice, so you can see exactly where your configuration drifts from a secure baseline.

  • Practical remediation advice: Actionable, specific guidance on how to fix each finding, not generic best-practice statements, but steps tailored to your environment. This is the part clients tell us they value most.

  • Debrief and support: The report isn’t the end of the conversation. We walk your team through the findings in a debrief session, answer their questions, and stay on hand as you work through remediation.

See a sample report

Want to see the quality of our reporting before you commit? Download an anonymised sample cloud penetration testing report and see exactly what you’ll receive: the structure, the depth of detail, and the clarity of our remediation advice.

Green technical background

START HERE

Not sure which test you need?

Most people searching “pen test” aren’t sure yet, that’s normal. Pick the closest match, or talk it through directly with a tester. We can incorporate multiple testing types for a single project. We often do web app + network testing if a business wants to cover both.
Three men laughing looking at a laptop in meeting room

Web Application Pen Testing

Customer-facing apps, portals and API layers.

Great for SAAS businesses.

Man with codeshield shirt looking at screen of penetration testing report

Network Penetration Testing

Internal and external infrastructure, patch…

Great for network heavy businesses.

Man with codeshield shirt looking at screen of penetration testing report

Cloud Penetration Testing

AWS, Azure, GCP and more environments.

Great for businesses operating in the cloud.

Man looking at penetration testing screen

AI / LLM Penetration Testing

Prompt injection, ISO 42001 readiness.

Great for applications incorporating AI

Two men shaking hands in front of TV

Social Engineering

Phishing, Vishing, SMShing and more.

Great for businesses with staff on the front line.

Three employees looking at each other

Mobile Application Pen Testing

Customer-facing apps, portals and API layers.

Great for apps on IOS & Android

Still not certain? Tell us what you’re building and we’ll scope it with you on a 15-minute call.

When do you need a cloud penetration test?

Cloud penetration testing isn’t a one-off box to tick. It’s something to build into the key moments in your cloud journey. You should consider a test when:

  • You’re migrating to the cloud or moving new workloads: validate your security before and after migration, when misconfigurations are most likely to appear.
  • You’re launching a new cloud-hosted application or service: test before it’s exposed to real users and real attackers, not after.
  • You’re preparing for a compliance audit: ISO 27001, SOC 2, PCI DSS and similar frameworks expect independent testing as part of certification.
  • A customer or partner is asking for it: enterprise procurement and due diligence increasingly require evidence of cloud testing before they’ll sign.
  • You’ve made significant configuration or architecture changes: new services, IAM changes, or integrations can introduce risks that weren’t there before.
  • You’ve had a security incident: verify that the gap is closed and check for anything else an attacker may have reached.
  • It’s simply been a while: best practice is at least once a year. If you can’t remember your last test, you’re overdue.

Not sure which of these applies to you? A quick scoping conversation will tell you what you need, and just as importantly, what you don’t.

LIVE REPORTING

Stay informed throughout your penetration test with real-time access to findings through our secure client portal.

As vulnerabilities are identified, they’re immediately available for your team to review, giving you complete visibility into the assessment as it progresses. Any High or Critical findings are communicated straight away via your agreed contact channels, ensuring urgent risks are never left waiting until the final report.

Our collaborative approach also allows for interactive re-testing during the engagement. As fixes are implemented, our consultants can validate them in real time, helping to reduce outstanding vulnerabilities before testing is complete.

At the end of the engagement, your portal is updated with the final quality-assured report, providing a comprehensive record of the assessment, findings, remediation guidance, and supporting evidence.

SQL Injection Example

TRUSTED UK PENETRATION TESTERS

Contact CodeShield today to get a quote or work with us

At CodeShield, our UK penetration testing team brings 20+ years of combined expertise delivering practical, results-driven security solutions tailored to your business.

Get a FREE penetration test quote today

Crest Member Logo
OSCP Logo
Crest LOGO

Cloud penetration testing FAQs

Do you offer retesting after we fix the issues?2026-07-27T07:27:50+00:00

Yes. Our support doesn’t end at the report. Once you’ve addressed the findings, we can retest to confirm the fixes are effective, giving you and your stakeholders verified assurance that the risks have been closed.

How does the shared responsibility model affect testing?2026-07-27T07:27:38+00:00

Cloud providers secure the underlying infrastructure, but securing how you configure and use their services is your responsibility. Our testing focuses squarely on that customer side, where the vast majority of cloud breaches actually occur.

Do you need permission from the cloud provider to test?2026-07-27T07:27:26+00:00

Most major providers now permit customer-authorised penetration testing of your own environment, though some activities carry specific rules. We handle this as part of scoping, ensuring all testing stays within your provider’s acceptable use policies.

What’s the difference between cloud penetration testing and traditional penetration testing?2026-07-27T07:27:15+00:00

Traditional testing simulates attacks against applications and infrastructure. Cloud penetration testing goes deeper into cloud-specific concerns, reviewing IAM policies, storage configurations, and platform settings within AWS, Azure, and Google Cloud to reduce the risk of a breach caused by misconfiguration.

Which cloud platforms do you test?2026-07-27T07:27:06+00:00

We have extensive experience across AWS, Azure, and Google Cloud, and we also support hybrid and multi-cloud environments. Every engagement is tailored to the platforms and services you actually use.

How much does cloud penetration testing cost?2026-07-27T07:25:56+00:00

The cost depends on scope: the cloud platforms involved, the size and complexity of your environment, and the depth of testing required. Rather than quote a misleading flat rate, we scope every engagement individually so you only pay for testing that delivers real value. Get in touch for a tailored quote.
Go to Top