Penetration Testing for eCommerce2026-09-24T10:41:58+00:00

Penetration Testing for eCommerce

CodeShield delivers CREST-accredited penetration testing for online retailers across the UK, from independent DTC brands and WooCommerce and Magento stores to high-traffic marketplaces, subscription businesses and B2B commerce platforms.

FREE penetration test for manufacturers quote

Crest Member Logo
OSCP Logo
Crest LOGO

CREST-accredited penetration testing Services

CREST-accredited penetration testing for eCommerce

Your checkout is the single most valuable target you own. It’s where money moves, where card details are entered, and where a customer’s personal data sits waiting to be exposed. Attackers know this, which is why online stores face a threat profile unlike almost any other business.

The attacks are specific to how you trade. Magecart and web-skimming crews inject a few lines of JavaScript into a checkout and quietly harvest card details from real customers for months. Credential-stuffing bots hammer your login pages to take over accounts and drain loyalty balances. Fraudsters test stolen cards against your payment flow, abuse discount and coupon logic, and manipulate prices and carts through flaws in your business rules. And the third-party scripts you rely on, payment widgets, analytics, chat and marketing tags, quietly widen your attack surface with every one you add.

On top of all that, if you take card payments you’re bound by PCI DSS, which requires penetration testing at least annually and after any significant change, and now expects you to manage and monitor the client-side scripts running on your payment pages.

Our penetration testing is built around that reality. Whether you’re testing to protect card data, to keep your store online through peak trading, to satisfy PCI DSS, or to reassure a partner or insurer, every engagement is scoped around your platform and the threats your store actually faces.

You work directly with a qualified tester who understands that your store is live revenue, not a lab, and that testing has to be planned around real customers and real sales.

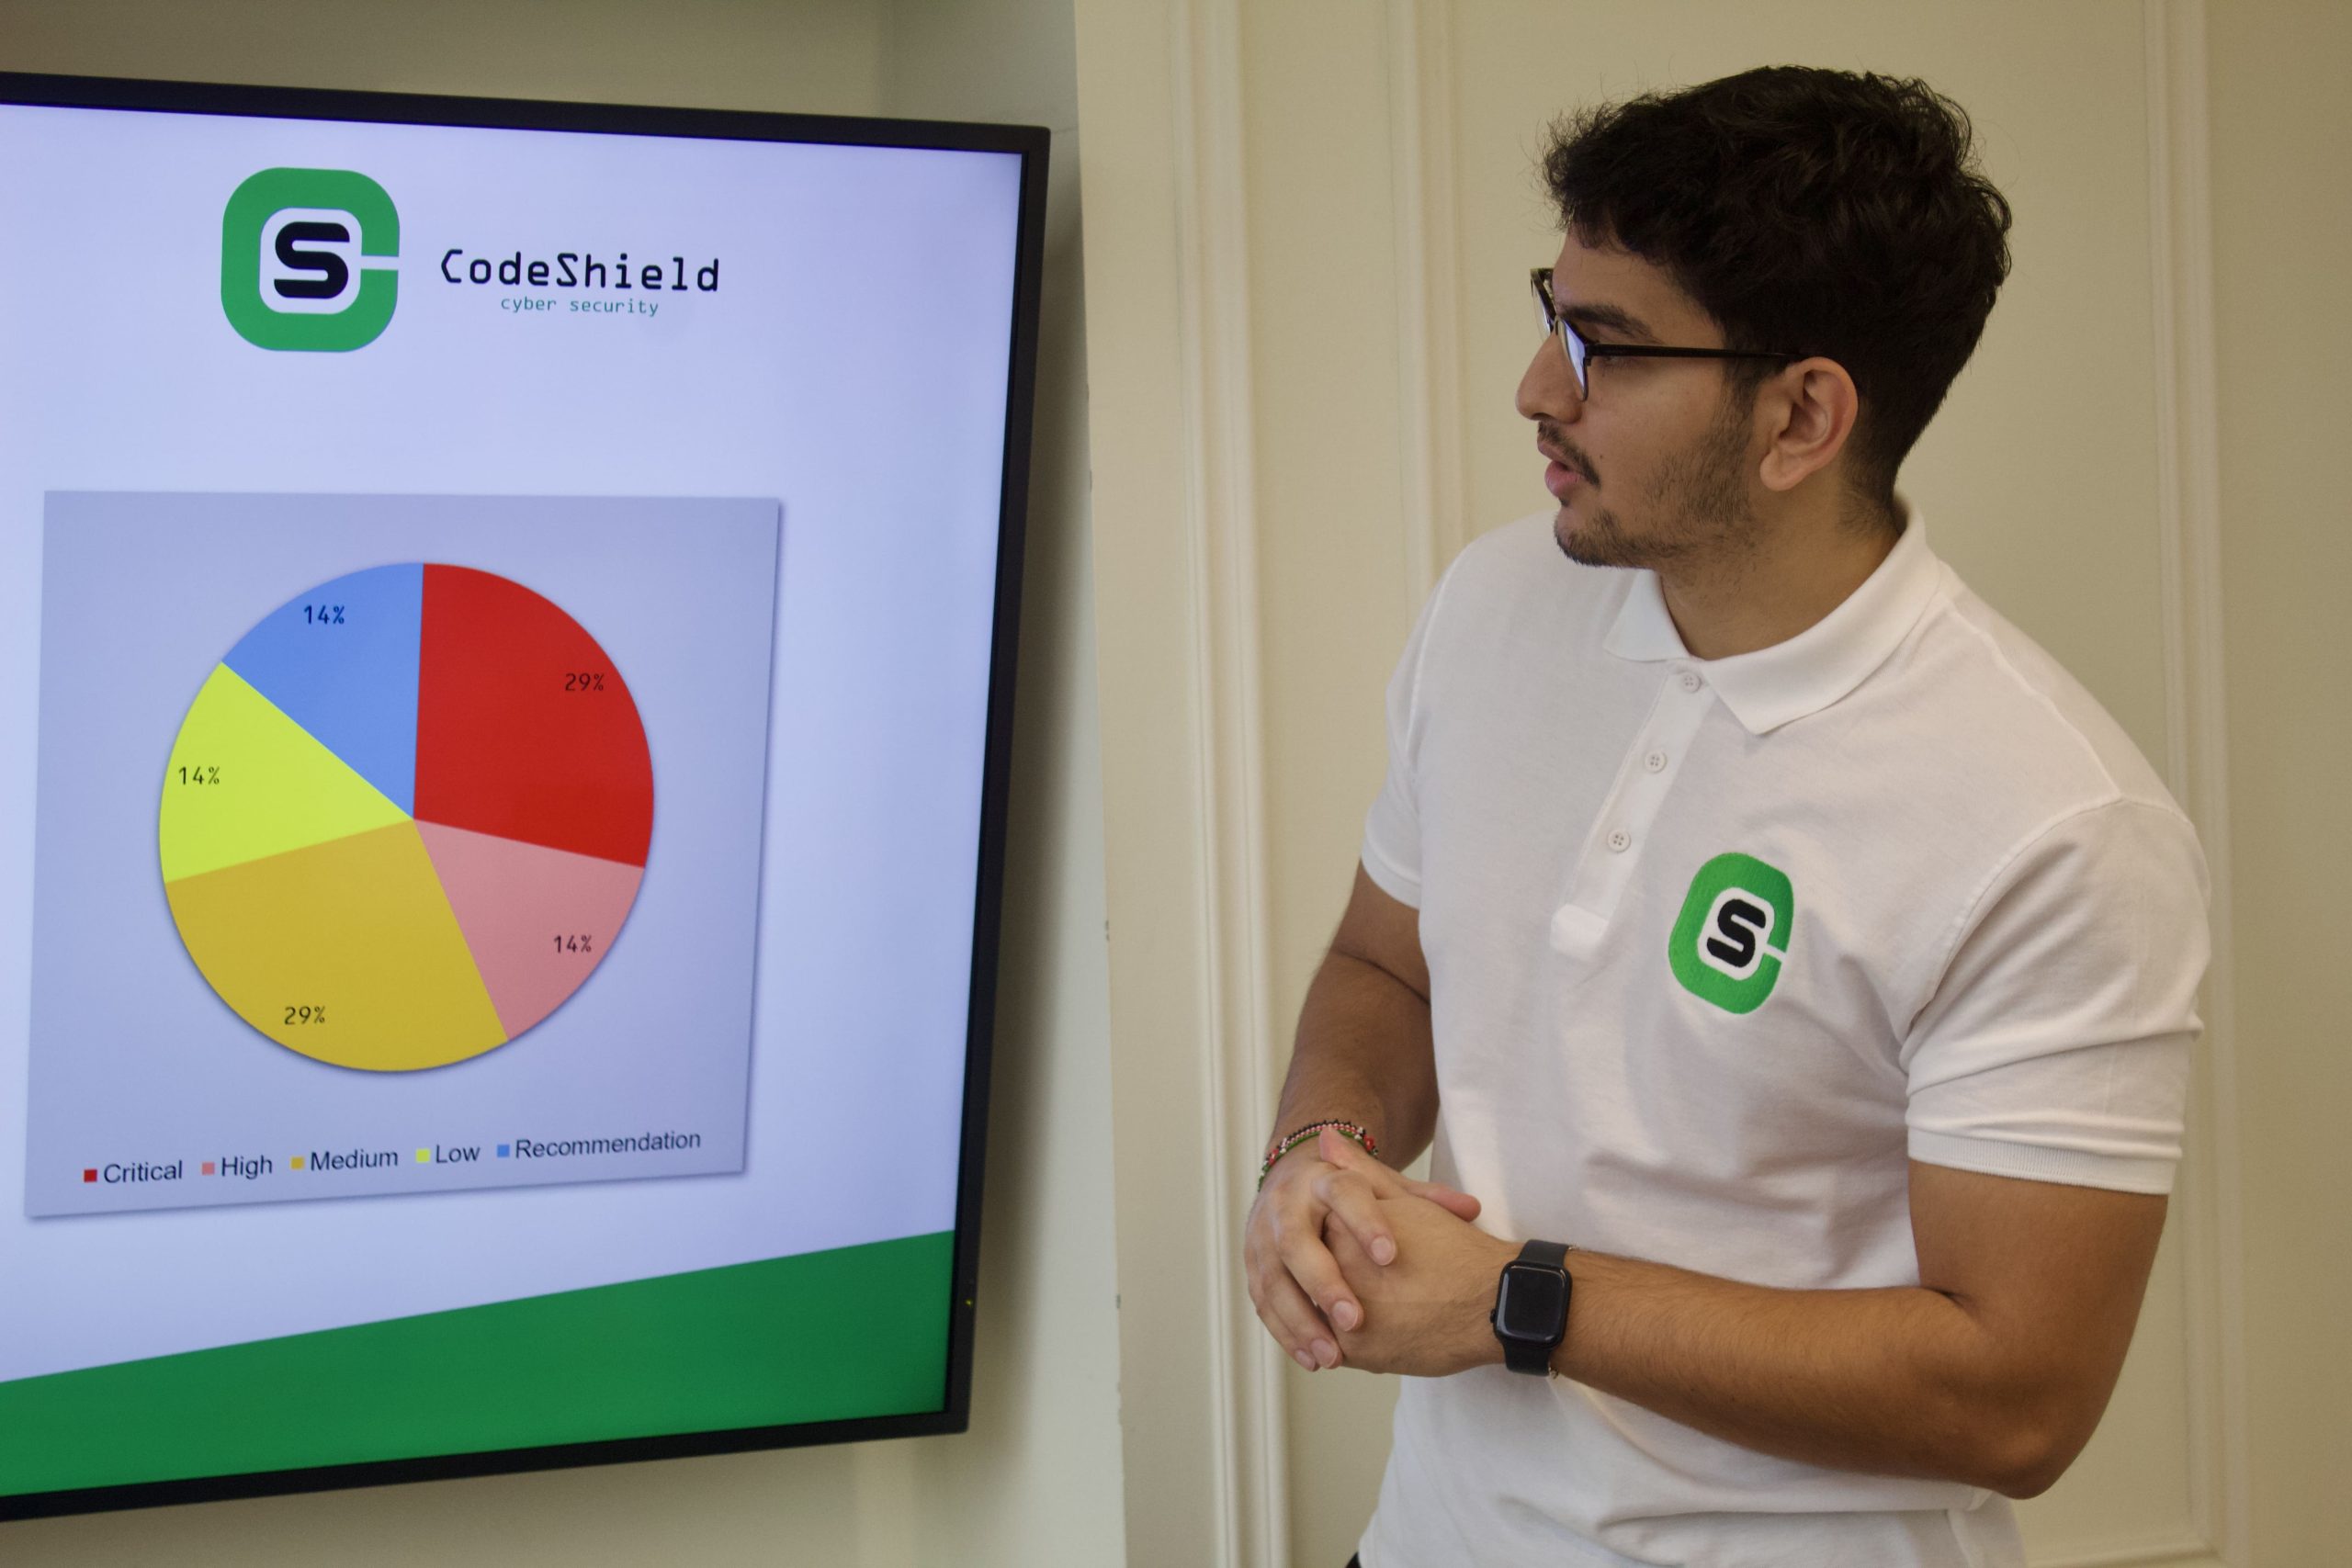
Man with codeshield shirt looking at screen of penetration testing report
Tom Sabine in front of web application assessment report

The full range of penetration testing for eCommerce

Different parts of your store face different threats, so we don’t take a one-size-fits-all approach. Choose a single targeted assessment or combine services for full coverage, from the storefront your customers see to the infrastructure and APIs behind it.

  • Web Application Penetration Testing: The core test for any online store. We test your storefront, checkout, customer accounts, and the business logic behind pricing, discounts, baskets and returns, for issues such as injection flaws, broken authentication, insecure APIs and logic abuse that lets an attacker pay less, take over accounts or reach data they shouldn’t. Essential for every retailer, on every platform.

  • Network Penetration Testing: We assess the infrastructure behind your store, servers, firewalls, hosting and remote access, and we check the boundary around your cardholder data environment. Proper segmentation is what keeps your PCI DSS scope, and your risk, contained. Best suited to retailers with their own hosting, self-managed platforms or complex back-end estates.

  • Cloud Penetration Testing: We evaluate the cloud environments most stores now run on, AWS, Azure, Google Cloud and Microsoft 365, for the misconfigurations, over-broad permissions and exposed services that lead to breaches of customer data, order records and admin systems.

  • LLM / AI Penetration Testing: We test the AI tools retailers are adding to search, product recommendations, customer support and merchandising, targeting the threats traditional testing misses: prompt injection, data leakage, model manipulation and insecure integrations. Increasingly relevant as AI features move into the buying journey.

  • Social Engineering Testing: Your store is only as secure as the people with backend access. Phishing an admin, a developer or a support agent can hand an attacker the keys to your CMS or payment settings. We test how your team stands up to phishing, pretexting and other human-focused attacks, then help you close the gaps.

  • Mobile Application Penetration Testing: We test iOS and Android shopping apps for insecure data storage, weak encryption and API vulnerabilities, essential for any retailer selling through an app as well as the web.

START HERE

Not sure which test you need?

Most people searching “pen test” aren’t sure yet, and that’s normal. Pick the closest match, or talk it through directly with a tester. We can combine multiple testing types in a single project, and for online stores we most often pair web application and network testing to cover both the storefront and the infrastructure behind it.
Three men laughing looking at a laptop in meeting room

Web Application Pen Testing

Customer-facing apps, portals and API layers.

Great for SAAS businesses.

Man with codeshield shirt looking at screen of penetration testing report

Network Penetration Testing

Internal and external infrastructure, patch…

Great for network heavy businesses.

Man with codeshield shirt looking at screen of penetration testing report

Cloud Penetration Testing

AWS, Azure, GCP and more environments.

Great for businesses operating in the cloud.

Man looking at penetration testing screen

AI / LLM Penetration Testing

Prompt injection, ISO 42001 readiness.

Great for applications incorporating AI

Two men shaking hands in front of TV

Social Engineering

Phishing, Vishing, SMShing and more.

Great for businesses with staff on the front line.

Three employees looking at each other

Mobile Application Pen Testing

Customer-facing apps, portals and API layers.

Great for apps on IOS & Android

Still not certain? Tell us what you’re building and we’ll scope it with you on a 15-minute call.

WHY TRUST CODESHIELD

Trusted & Independently verified.

Crest Accreditation Logo

“Tom and team helped greatfully to arrange our pentest to suit our scope and requirements. We will be working with them again in the near future for further tests. Well done guys.”

Adrian Morris

“Excellent service, fast turnaround, and very reasonable cost. CREST-approved testing carried out professionally from start to finish. Highly recommended.”

Matt Bell

“Did a great job on our latest pen test. The team was very helpful, knowledgeable and professional. 100% recommend!”

Billy Carey

Penetration testing for online stores of every shape and size

Retailers come to us because a single incident can leak card data, hand over customer accounts, or take the store offline at the worst possible moment. Our testing supports:

  • Independent and DTC brands: protecting your checkout, your customer list and your reputation without an in-house security team.
  • WooCommerce and WordPress stores: testing the platform, plugins and custom code that make up the biggest ecommerce footprint on the web.
  • Magento and Adobe Commerce stores: independent testing of a platform that is powerful, heavily customised and frequently targeted.
  • Custom, headless and composable builds: securing bespoke storefronts and the APIs that stitch them together.
  • Marketplaces and multi-vendor platforms: assessing the added risk that comes with third-party sellers and shared infrastructure.
  • Subscription and recurring-billing businesses: protecting stored payment details and the billing logic behind them.
  • B2B ecommerce and wholesale portals: securing account-based ordering, credit terms and customer-specific pricing.
  • High-traffic and seasonal-peak retailers: testing before the traffic arrives, so Black Friday isn’t the day you find out.

If you take card payments online, hold customer data, or depend on your store staying up to make money, our penetration testing for eCommerce is built for you.

Three men laughing looking at a laptop in meeting room

Meet your compliance requirements with confidence

Many retailers first come to us because PCI DSS, an acquiring bank, a partner or an insurer requires an independent test. We make that requirement straightforward to satisfy, and turn a tick-box exercise into genuine security improvement.

  • PCI DSS: independent penetration testing to meet the standard’s requirement for annual testing and testing after significant change, covering both your applications and the segmentation around your cardholder data environment. We also help you get ahead of the client-side script and change-monitoring expectations introduced in PCI DSS v4.0.

  • Cyber Essentials & Cyber Essentials Plus: hands-on assessment beyond the self-certified baseline, increasingly expected by partners and B2B customers.

  • ISO 27001: independent testing to evidence your information security controls.

  • SOC 2: supporting the security testing expected of platform and B2B commerce providers selling into larger customers.

  • UK GDPR & the Data Protection Act 2018: demonstrating appropriate technical measures for the customer and order data you hold.

  • Professional indemnity & cyber insurance: satisfying the security questions insurers now ask before they renew or quote.

You’ll receive a clear, audit-ready report that maps findings to what your framework actually asks for, with practical remediation advice to close the gaps, not just document them.

WHY CODESHIELD – 20+ YEARS EXPERIENCE

You work with the person doing the testing.

At CodeShield, our UK penetration testing team brings 20+ years of combined expertise delivering practical, results-driven security solutions tailored to your business.

You work directly with a fully-qualified pen tester. You meet them before you pay, so you know who you’re working with.

  • Find & Fix Vulnerabilities: Uncover hidden threats with expert-led testing and gain true confidence in your security.
  • Simplify Compliance: Navigate ISO, PCI DSS, SOC 2 & DSPT with clear, actionable guidance, not just box-ticking.
  • Strengthen Your Defences:  Prioritise real risks and improve your security posture with insights from seasoned professionals.
  • Save Time & Reduce Complexity: We handle the technical details, letting you stay focused on your business.
Two men looking at a laptop in a meeting room

Our Values

Open Mindedness

We believe there’s no single solution to a security challenge. By staying open to new ideas and approaches, our teams find the best outcomes for every unique obstacle we face.

Honesty & Integrity

We believe there’s no single solution to a security challenge. By staying open to new ideas and approaches, our teams find the best outcomes for every unique obstacle we face.

Professionalism

We believe there’s no single solution to a security challenge. By staying open to new ideas and approaches, our teams find the best outcomes for every unique obstacle we face.

Collaboration

We believe there’s no single solution to a security challenge. By staying open to new ideas and approaches, our teams find the best outcomes for every unique obstacle we face.

What’s in your penetration testing report

The report is where a penetration test earns its value. A test is only as useful as the document that comes out of it, and ours are built to be read and acted on, not filed away. Every engagement ends with a clear, structured report that works for your developers and your senior stakeholders alike.

  • Executive summary: A plain-English overview of what we tested, what we found, and what it means for your business, written so a non-technical reader can understand your risk position in a couple of minutes.

  • Risk-prioritised findings: Every vulnerability and misconfiguration we identify, rated by severity and real-world impact, so you know exactly what to fix first. No noise, no padding, just the issues that matter, in the order they matter.

  • Technical detail and proof of concept: For each finding, a clear explanation of the issue, proof-of-concept evidence showing how it could be exploited, and everything your team needs to reproduce and verify it.

  • Benchmarking against best practice: Where relevant, findings are mapped against CIS benchmarks and cloud provider best practice, so you can see exactly where your configuration drifts from a secure baseline.

  • Practical remediation advice: Actionable, specific guidance on how to fix each finding, not generic best-practice statements, but steps tailored to your environment. This is the part clients tell us they value most.

  • Debrief and support: The report isn’t the end of the conversation. We walk your team through the findings in a debrief session, answer their questions, and stay on hand as you work through remediation.

See a sample report

Want to see the quality of our reporting before you commit? Download an anonymised sample penetration testing report and see exactly what you’ll receive: the structure, the depth of detail, and the clarity of our remediation advice.

Green technical background

When does an online store need a penetration test?

Penetration testing isn’t a one-off box to tick. It’s something to build into the key moments of your business. You should consider a test when:

  • You’re launching or replatforming your store: test the new build before it’s exposed to real customers and real card details, not after.

  • PCI DSS requires it: the standard expects testing at least annually and after any significant change to your environment.

  • You’re preparing for an ISO 27001 or Cyber Essentials assessment: these frameworks expect independent testing as part of certification.

  • A partner, acquiring bank or insurer is asking for it: due-diligence and renewal processes increasingly require evidence of penetration testing before anyone will proceed.

  • You’ve added new payment methods, integrations or third-party scripts: every new tag, plugin or connection can introduce vulnerabilities that weren’t there before.

  • You’ve had an incident or a near miss: verify the gap is closed and check for anything else an attacker may have reached, particularly if you suspect skimming.

  • It’s simply been a while: best practice is at least once a year. If you can’t remember your last test, you’re overdue.

Not sure which of these applies to your store? A quick scoping conversation will tell you what you need, and, just as importantly, what you don’t.

LIVE REPORTING

Stay informed throughout your penetration test with real-time access to findings through our secure client portal.

Stay informed throughout your penetration test with real-time access to findings through our secure client portal.

As vulnerabilities are identified, they’re immediately available for your team to review, giving you complete visibility into the assessment as it progresses. Any High or Critical findings are communicated straight away via your agreed contact channels, so urgent risks are never left waiting until the final report.

Our collaborative approach also allows for interactive re-testing during the engagement. As fixes are implemented, our consultants can validate them in real time, helping to reduce outstanding vulnerabilities before testing is complete.

At the end of the engagement, your portal is updated with the final quality-assured report, providing a comprehensive record of the assessment, findings, remediation guidance and supporting evidence.
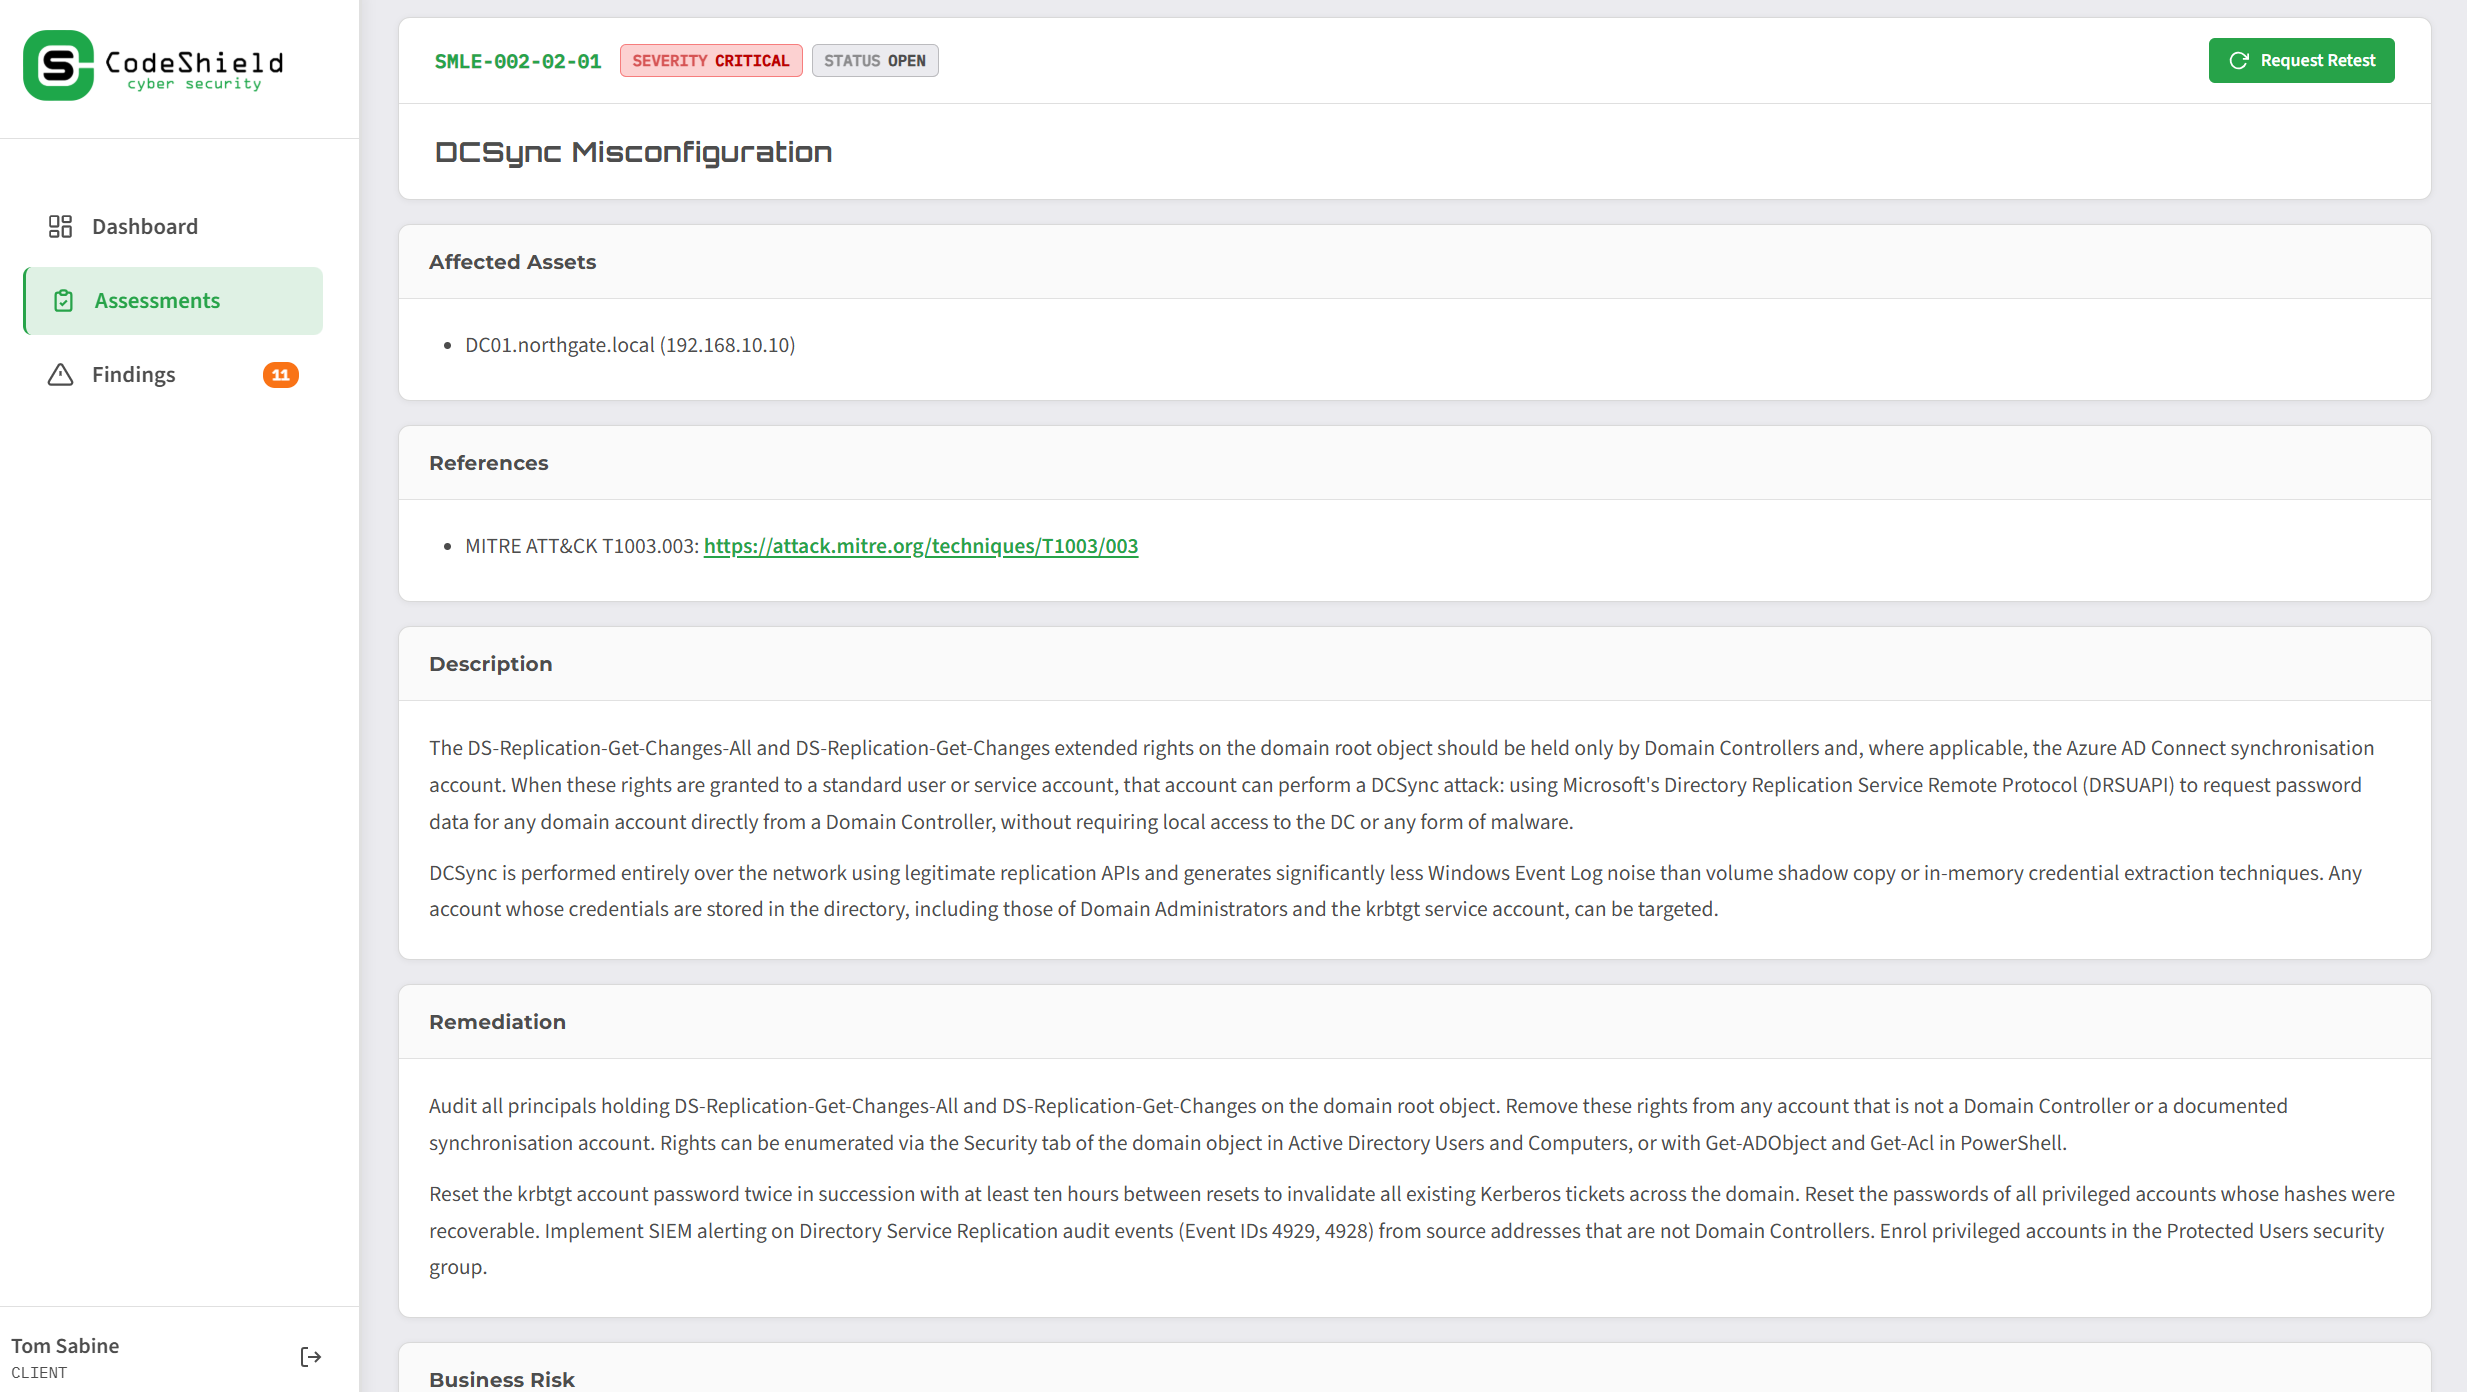
DCSync Finding

TRUSTED UK PENETRATION TESTERS

Contact CodeShield today for penetration testing for eCommerce

At CodeShield, our UK penetration testing team brings 20+ years of combined expertise, delivering practical, results-driven security tailored to your store.

Get a FREE penetration test quote today

Crest Member Logo
OSCP Logo
Crest LOGO

Penetration testing FAQs

Do you test the model or the application around it?2026-07-27T10:41:27+00:00

Both. A secure model in an insecure application is still a risk, and vice versa. We assess the model’s behaviour, the application logic, the data pipelines, any connected tools or agents, and the supporting infrastructure, giving you a complete picture.

Will testing disrupt our network or cause downtime?2026-07-27T08:41:58+00:00

Our testing is designed to minimise disruption. We agree all rules of engagement with you during scoping, and where any activity carries a risk to stability, we plan it carefully and keep you informed throughout.

Can you test third-party models like GPT, Claude, or Gemini?2026-07-27T10:41:38+00:00

Yes. Most organisations build on commercial models rather than training their own, so we focus on how you’ve implemented and integrated that model, your prompts, data connections, guardrails, and permissions, which is where the risks you can actually control live.

Do you offer retesting after we fix the issues?2026-07-27T07:27:50+00:00

Yes. Our support doesn’t end at the report. Once you’ve addressed the findings, we can retest to confirm the fixes are effective, giving you and your stakeholders verified assurance that the risks have been closed.

What’s the difference between mobile app and web app penetration testing?2026-07-20T08:39:16+00:00

Web app testing focuses on browser-based applications, while mobile app testing adds device-specific concerns such as insecure local data storage, binary protections, reverse engineering, and platform configuration, alongside testing the APIs and backend the app relies on.

Do you offer retesting after we fix the issues?2026-07-27T08:42:08+00:00

Yes. Our support doesn’t end at the report. Once you’ve addressed the findings, we can retest to confirm the fixes are effective, giving you and your stakeholders verified assurance that the risks have been closed.

Will testing disrupt our live app or users?2026-07-20T08:39:38+00:00

No. Wherever possible we test against a non-production environment such as UAT or QA, so there’s no risk to your live service. If that isn’t possible, we take a more cautious approach to post-exploitation testing to protect your users.

Do you offer retesting after we fix the issues?2026-07-27T09:03:02+00:00

Yes. Our support doesn’t end at the report. Once you’ve addressed the findings, we can retest to confirm the fixes are effective, giving you and your stakeholders verified assurance that the risks have been closed.

Go to Top