



CREST-accredited penetration testing Services for fintech
CREST-accredited penetration testing for the fintech sector
Fintech sits at the intersection of everything an attacker wants: money in motion, high-value personal and financial data, and a fast-moving technology stack built on APIs, cloud infrastructure and third-party integrations. A single flaw in a transfer flow, an over-permissioned API or a weak authentication step can expose customer funds or bring the regulator to your door.
Our penetration testing for fintech is tailored to that reality. Whether you’re testing to protect customer money and card data, to satisfy PCI DSS, SOC 2 or ISO 27001, to support your FCA obligations, or to pass the due diligence of a bank partner or enterprise buyer, every engagement is scoped around your architecture and the real-world threats your platform actually faces.
You work directly with a qualified tester who understands payment flows, open banking and the business-logic attacks that generic scanners miss, not a call centre and not an offshore checklist.

The full range of penetration testing for fintech.
Most teams searching for “penetration testing for fintech” aren’t yet certain what they need, that’s completely normal. Pick the closest match below, or talk it through with a tester. We can combine several testing types in a single engagement, and for a fintech we very often do: web application plus API testing to cover the customer-facing product, and network or cloud testing to cover the environment it runs in.
START HERE
Not sure which test you need?
Different systems face different threats, so we don’t take a one-size-fits-all approach. Choose a single targeted assessment or combine services for full coverage across your platform’s attack surface.
WHY TRUST CODESHIELD
Trusted & Independently verified.

Penetration testing for fintech, whatever you’re building
Fintechs come to us because security isn’t optional in their world, it’s a licence to operate and a condition of winning enterprise deals. Our penetration testing for the fintech sector supports:
- Payments & payment gateways: securing card flows, transaction processing and the cardholder-data environment under PCI DSS.
- Neobanks & challenger banks: protecting core banking systems, customer accounts and the funds that move through them.
- Lending, credit & BNPL platforms: testing application journeys, decisioning logic and the personal and financial data behind them.
- Open banking & TPPs (AISPs / PISPs): securing the APIs and consent flows at the heart of PSD2 and open banking.
- Crypto & digital-asset platforms: assessing wallets, exchanges and the infrastructure that holds high-value assets.
- WealthTech & robo-advisors: protecting portfolios, client money and sensitive investment data.
- InsurTech & RegTech: securing the platforms that hold high-value personal, claims and compliance data.
- Embedded finance & Banking-as-a-Service: testing the APIs and integrations you expose to partners building on top of you.
If your platform moves money, holds card or account data, or sells into banks, enterprises and regulated markets, our penetration testing for fintech is built for you.

Meet your compliance requirements with confidence
Many fintechs first come to us because a framework, auditor, bank partner or enterprise customer requires an independent test. We make that requirement straightforward to satisfy, and turn a tick-box exercise into genuine security improvement.
Our penetration testing for fintech supports:
You’ll receive a clear, audit-ready report that maps findings to what your framework actually asks for, with practical remediation advice to close the gaps, not just document them.
WHY CODESHIELD – 20+ YEARS EXPERIENCE
You work with the person doing the testing.
At CodeShield, our UK penetration testing team brings 20+ years of combined expertise delivering practical, results-driven security solutions tailored to your business.
You work directly with a fully-qualified pen tester. You meet them before you pay, so you know who you’re working with.

Our Values
What’s in your penetration testing report
The report is where a penetration test earns its value. A test is only as useful as the document that comes out of it, and ours are built to be read and acted on, not filed away. Every penetration testing for fintech engagement ends with a clear, structured report that works for your engineers, your compliance team and your investors alike.
See a sample report
Want to see the quality of our reporting before you commit? Download an anonymised sample penetration testing report and see exactly what you’ll receive: the structure, the depth of detail, and the clarity of our remediation advice.

When does a fintech need a penetration test?
Penetration testing for fintech isn’t a one-off box to tick, it’s something to build into the key moments of your business. You should consider a test when:
Not sure which of these applies to you? A quick scoping conversation will tell you what you need, and, just as importantly, what you don’t.
LIVE REPORTING
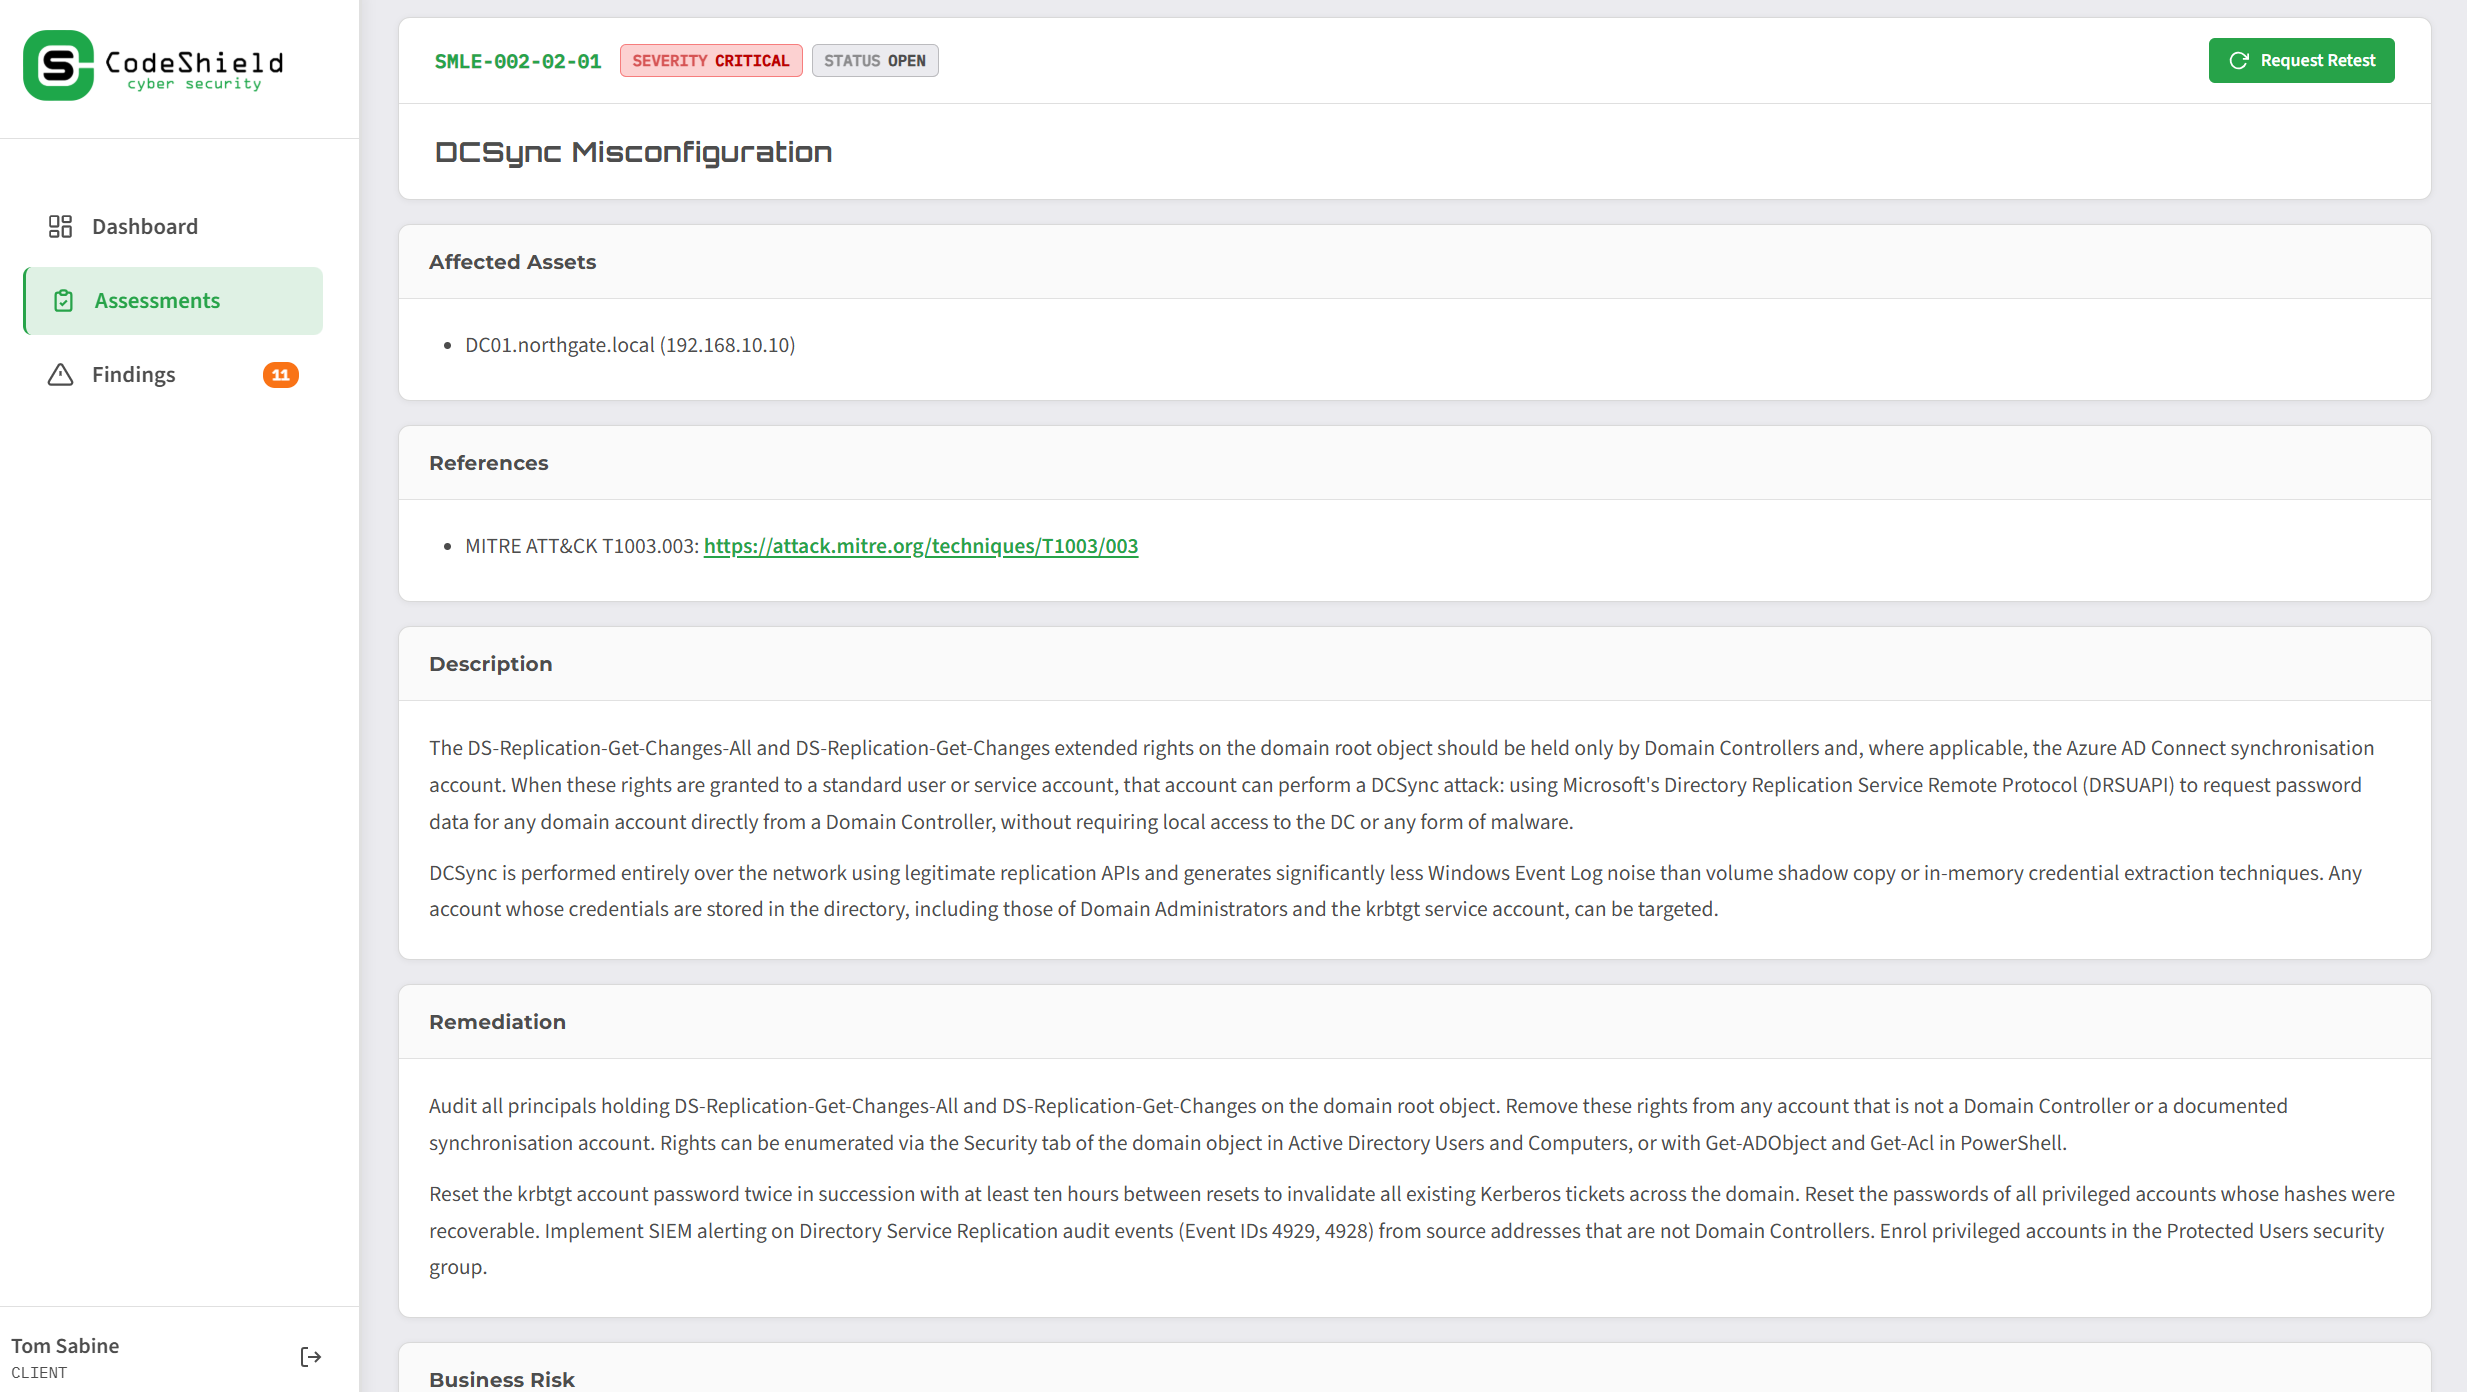
Stay informed throughout your penetration test with real-time access to findings through our secure client portal.
As vulnerabilities are identified, they’re immediately available for your team to review, giving you complete visibility into the assessment as it progresses. Any High or Critical findings are communicated straight away via your agreed contact channels, ensuring urgent risks are never left waiting until the final report.
Our collaborative approach also allows for interactive re-testing during the engagement. As fixes are implemented, our consultants can validate them in real time, helping to reduce outstanding vulnerabilities before testing is complete.
At the end of the engagement, your portal is updated with the final quality-assured report, providing a comprehensive record of the assessment, findings, remediation guidance, and supporting evidence.
TRUSTED UK PENETRATION TESTERS
Contact CodeShield today for penetration testing for fintech
At CodeShield, our UK penetration testing team brings 20+ years of combined expertise, delivering practical, results-driven security tailored to your platform.
Penetration testing FAQs
We start with a scoping conversation to understand your environment, objectives, and any constraints. Together we define exactly what’s being tested, the rules of engagement, and the timeline, ensuring the test aligns with your goals while minimising any risk of disruption.
Wherever possible we test in a staging or non-production environment to avoid any disruption. If production testing is necessary, we agree all precautions with you during scoping to keep your application stable throughout.
Industry best practice is to test at least annually, and after any significant change to your infrastructure. Frameworks such as PCI DSS and ISO 27001 typically require annual testing. We’ll help you define the right cadence for your organisation.
AI penetration testing is a security assessment of the systems you build around artificial intelligence, particularly large language models. It focuses on the risks unique to AI, such as prompt injection, data leakage, and models being manipulated into unsafe behaviour, alongside the security of the application and infrastructure around them.
Industry best practice is to test at least annually, and after any significant change to your infrastructure or applications. Frameworks such as PCI DSS and ISO 27001 typically require annual testing. We’ll help you define the right cadence for your organisation.
Yes. Each platform has its own risks and security model, so we test both with platform-specific expertise. If your app is on one platform or both, we tailor the engagement to match.
In black box testing the tester has no prior knowledge of the application. In white box testing they have full access to code and documentation. Grey box sits in between, with partial knowledge for a realistic yet efficient assessment. We’ll help you choose the right approach for your goals during scoping.
