



CREST-accredited penetration testing Services
CREST-accredited penetration testing for SaaS companies
A SaaS platform concentrates risk in a way few other businesses do. You hold many customers’ data in one system, behind one login, on one shared infrastructure. That’s the whole value of the model, and it’s exactly why a single flaw can matter so much: a broken access control or a weak point in tenant isolation doesn’t expose one account, it potentially exposes all of them.
The threats are specific to how you’re built. Attackers probe authentication and session handling, look for object-level access flaws that let one user reach another’s data, and target the APIs your product and integrations run on. Cloud misconfigurations, over-permissioned IAM roles and exposed storage turn a small mistake into a large breach. And because your platform is always on and always changing, every release is a new opportunity to introduce something exploitable.
There’s a commercial dimension too. Your customers now ask for security evidence before they buy. Enterprise procurement teams send security questionnaires, ask for your SOC 2 report, and want to know when you last had an independent penetration test. For most SaaS companies, testing isn’t only a security necessity, it’s what unblocks the deal.
Our penetration testing is built around that reality. Whether you’re testing to protect customer data, to satisfy SOC 2 or ISO 27001, or to get past a prospect’s security review, every engagement is scoped around your architecture and the threats your platform actually faces.
You work directly with a qualified tester who understands multi-tenancy, APIs and modern cloud stacks, and who plans testing around your release cycle and environments, not a call centre and not an offshore checklist.

START HERE
Not sure which test you need?
Most people searching “pen test” aren’t sure yet, and that’s normal. Pick the closest match, or talk it through directly with a tester. We can combine multiple testing types in a single project, and for SaaS companies we most often pair web application and cloud testing to cover both the product and the infrastructure behind it.
WHY TRUST CODESHIELD
Trusted & Independently verified.

Penetration testing for SaaS at every stage
Software companies come to us because a single incident can expose customer data, fail a security review, or cost you a deal you’ve spent months chasing. Our testing supports:
- Early-stage and startup SaaS: getting a first independent test and a shareable report so you can close enterprise deals that are gated on security.
- B2B SaaS platforms: meeting the security expectations of larger customers and their procurement teams.
- Vertical SaaS (fintech, healthtech, legaltech, proptech): testing to the raised bar that regulated and sensitive-data markets demand.
- Multi-tenant platforms: validating that tenant isolation genuinely holds, not just in theory.
- API-first and developer platforms: securing the APIs, webhooks and integrations your customers build on.
- Marketplaces and app platforms: assessing the added risk of third-party apps and extensions on your platform.
- Companies preparing for SOC 2 or ISO 27001: satisfying the independent testing these frameworks expect.
- Scale-ups going through due diligence: reassuring investors and acquirers about the security of what they’re backing.
If you hold customer data, run a multi-tenant platform, or need to get past enterprise security reviews, our penetration testing for SaaS is built for you.

Meet your requirements with confidence
Many SaaS companies first come to us because SOC 2, ISO 27001, a customer or an investor requires an independent test. We make that requirement straightforward to satisfy, and turn a tick-box exercise into genuine security improvement.
You’ll receive a clear, audit-ready report that maps findings to what your framework actually asks for, with practical remediation advice to close the gaps, not just document them.
WHY CODESHIELD – 20+ YEARS EXPERIENCE
You work with the person doing the testing.
At CodeShield, our UK penetration testing team brings 20+ years of combined expertise delivering practical, results-driven security solutions tailored to your business.
You work directly with a fully-qualified pen tester. You meet them before you pay, so you know who you’re working with.

Our Values
What’s in your penetration testing report
The report is where a penetration test earns its value. For a SaaS company it does double duty: it tells your developers what to fix, and it’s the document you hand to prospects and auditors. Ours are built to be read and acted on, not filed away, and they work for your technical team and your buyers alike.
See a sample report
Want to see the quality of our reporting before you commit? Download an anonymised sample penetration testing report and see exactly what you’ll receive: the structure, the depth of detail, and the clarity of our remediation advice.

When does a SaaS company need a penetration test?
Penetration testing isn’t a one-off box to tick. It’s something to build into the key moments of your business. You should consider a test when:
Not sure which of these applies to your platform? A quick scoping conversation will tell you what you need, and, just as importantly, what you don’t.
LIVE REPORTING
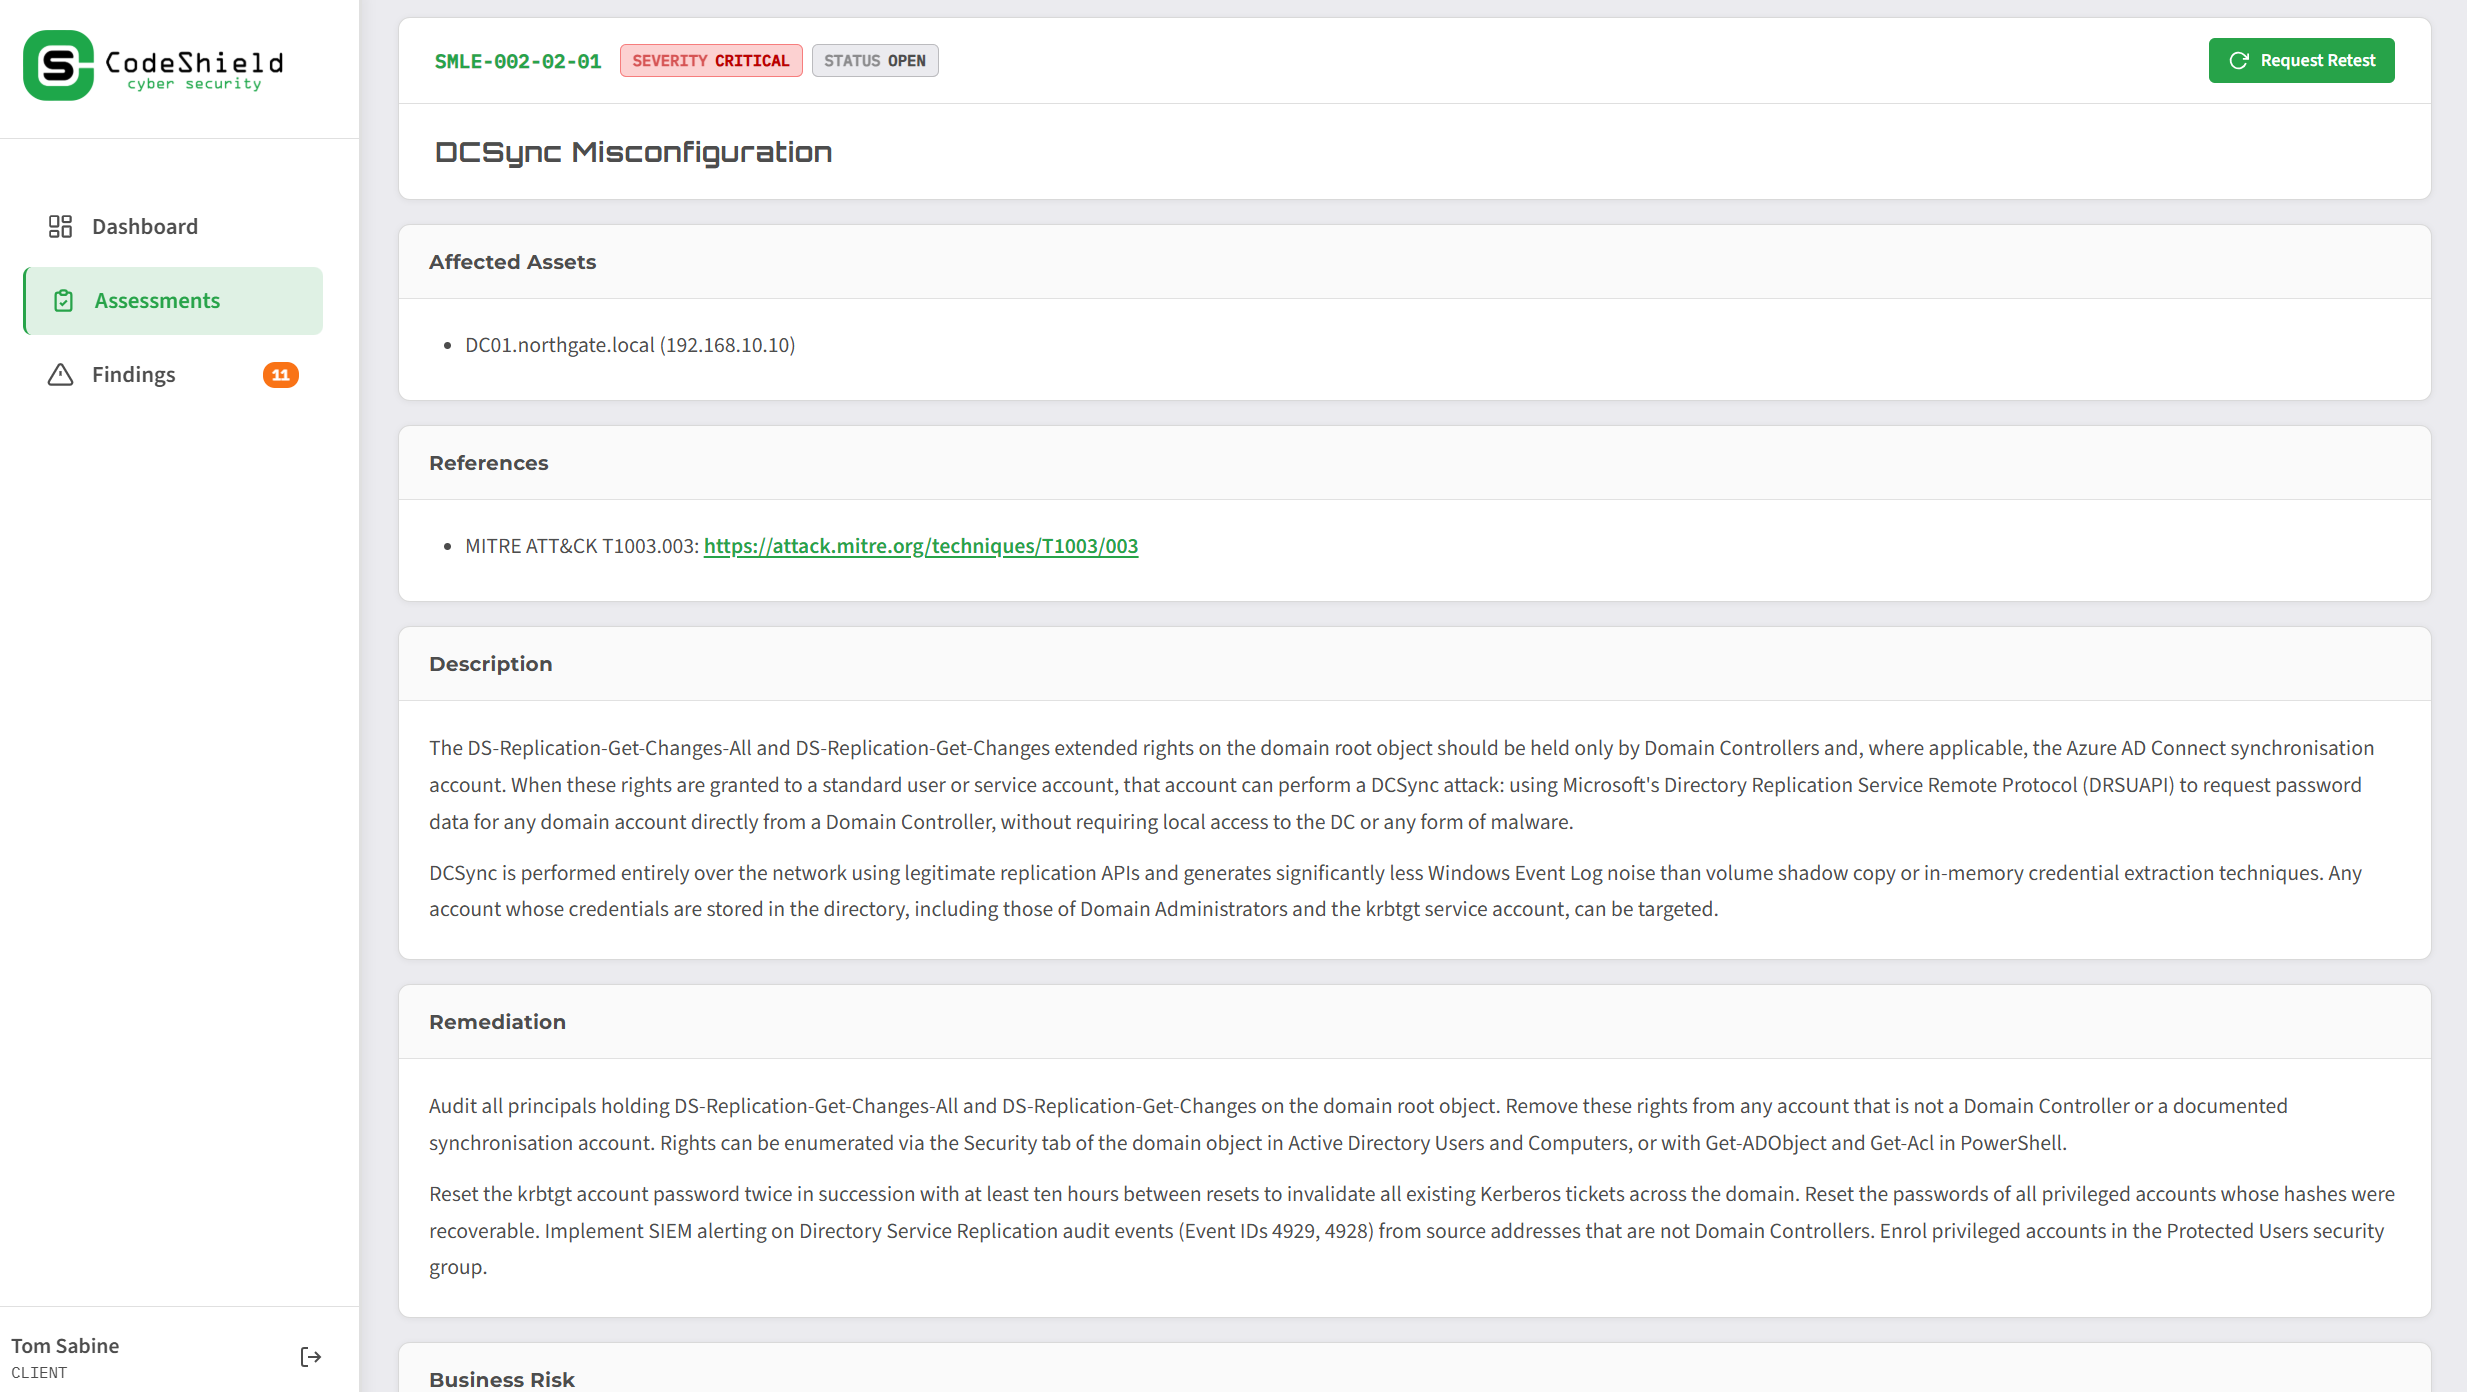
Stay informed throughout your penetration test with real-time access to findings through our secure client portal.
Stay informed throughout your penetration test with real-time access to findings through our secure client portal.
As vulnerabilities are identified, they’re immediately available for your team to review, giving you complete visibility into the assessment as it progresses. Any High or Critical findings are communicated straight away via your agreed contact channels, so urgent risks are never left waiting until the final report.
Our collaborative approach also allows for interactive re-testing during the engagement. As fixes are implemented, our consultants can validate them in real time, helping to reduce outstanding vulnerabilities before testing is complete.
At the end of the engagement, your portal is updated with the final quality-assured report, providing a comprehensive record of the assessment, findings, remediation guidance and supporting evidence.
TRUSTED UK PENETRATION TESTERS
Contact CodeShield today for penetration testing for SaaS
At CodeShield, our UK penetration testing team brings 20+ years of combined expertise, delivering practical, results-driven security tailored to your platform.
Penetration testing FAQs
No. Wherever possible we test against a non-production environment such as UAT or QA, so there’s no risk to your live service. If that isn’t possible, we take a more cautious approach to post-exploitation testing to protect your users.
A vulnerability scan is automated and flags known issues. A penetration test adds expert human analysis, actively exploiting weaknesses to understand the real business impact and uncovering the business-logic and chained vulnerabilities that scanners simply cannot find.
A vulnerability scan is automated and flags known issues. A penetration test adds expert human analysis, actively exploiting weaknesses to understand the real business impact and uncovering the misconfigurations, credential issues, and lateral movement paths that scanners simply cannot find.
Our testing is designed to minimise disruption. We agree all rules of engagement with you during scoping, and where any activity carries a risk to stability, we plan it carefully and keep you informed throughout.
Yes. Our support doesn’t end at the report. Once you’ve addressed the findings, we can retest to confirm the fixes are effective, giving you and your stakeholders verified assurance that the risks have been closed.
Yes. Our support doesn’t end at the report. Once you’ve addressed the findings, we can retest to confirm the fixes are effective, giving you and your stakeholders verified assurance that the risks have been closed.
