



CREST-accredited penetration testing Services in Newcastle
Penetration testing services in Newcastle
CodeShield delivers CREST-accredited penetration testing services to organisations across Newcastle, from B2B SaaS platforms and financial services firms to multi-site enterprises with complex internal networks. No generic checklists. No false positives. Just clear, credible results from a dedicated expert who guides you from scoping through to remediation.
Whether you’re testing to protect customer data, satisfy a compliance framework, or pass enterprise due diligence, every engagement is tailored to your environment and the real-world threats you actually face.

START HERE
Not sure which test you need?
Most people searching “pen test Newcastle” aren’t sure yet, that’s normal. Pick the closest match, or talk it through directly with a tester. We can incorporate multiple testing types for a single project. We often do web app + network testing if a business wants to cover both.
WHY TRUST CODESHIELD
Trusted & Independently verified.

Penetration testing services in Newcastle for regulated and security-conscious sectors
Our clients come to us because security isn’t optional in their world, it’s a condition of doing business. We work extensively with:
Software & data-driven businesses
- Financial Services & FinTech: protecting payment flows, customer accounts, and sensitive financial data under FCA and PCI DSS expectations.
- Legal Services: safeguarding confidential client and case data.
- Healthcare & Health Tech: securing patient data and supporting NHS DSP Toolkit and compliance requirements.
- Insurance: testing the platforms that hold high-value personal and claims data.
- HR & Payroll Software: protecting some of the most sensitive personal data any system holds.
Infrastructure-heavy and multi-site organisations
- Retail, Manufacturing, Logistics & Distribution: assessing larger internal networks, connected sites, and operational systems.
- Professional Services: protecting client data across distributed teams and remote access.
- Hospitality & Care Providers: securing multi-site networks, guest and resident data, and corporate Wi-Fi.
If you develop or maintain business-critical applications, handle sensitive customer or financial data, or sell into enterprise and regulated markets, our penetration testing services in Newcastle are built for you.

Meet your compliance requirements with confidence
Many organisations first come to us because a framework, auditor, or enterprise customer requires an independent penetration test. We make that requirement straightforward to satisfy, and turn a tick-box exercise into genuine security improvement.
Our penetration testing services in Newcastle support:
You’ll receive a clear, audit-ready report that maps findings to what your framework actually asks for, and practical remediation advice to close the gaps, not just document them.
WHY CODESHIELD – 20+ YEARS EXPERIENCE
You work with the person doing the testing.
At CodeShield, our UK penetration testing team brings 20+ years of combined expertise delivering practical, results-driven security solutions tailored to your business.
You work directly with a fully-qualified pen tester. You meet them before you pay, so you know who you’re working with.

Our Values
What’s in your penetration testing report
The report is where a penetration test earns its value. A test is only as useful as the document that comes out of it, and ours are built to be read and acted on, not filed away. Every engagement ends with a clear, structured report that works for your technical team and your senior stakeholders alike.
See a sample report
Want to see the quality of our reporting before you commit? Download an anonymised sample penetration testing report and see exactly what you’ll receive: the structure, the depth of detail, and the clarity of our remediation advice.

Penetration testing Newcastle. When do you need one?
Penetration testing in Newcastle isn’t a one-off box to tick. It’s something to build into the key moments of your business. You should consider a test when:
- You’re launching a new product, application, or feature: test before it’s exposed to real users and real attackers, not after.
- You’re preparing for a compliance audit: ISO 27001, SOC 2, PCI DSS, Cyber Essentials Plus and similar frameworks expect independent testing as part of certification.
- A customer or partner is asking for it: enterprise procurement and due diligence increasingly require evidence of penetration testing before they’ll sign.
- You’ve made significant infrastructure or code changes: migrations, new integrations, or major releases can introduce vulnerabilities that weren’t there before.
- You’re going through a merger, acquisition, or investment: understand the security posture of what you’re buying, or reassure the people investing in you.
- You’ve had a security incident: verify that the gap is closed and check for anything else an attacker may have reached.
- It’s simply been a while: best practice is at least once a year. If you can’t remember your last test, you’re overdue.
Not sure which of these applies to you? A quick scoping conversation will tell you what you need, and just as importantly, what you don’t.
LIVE REPORTING
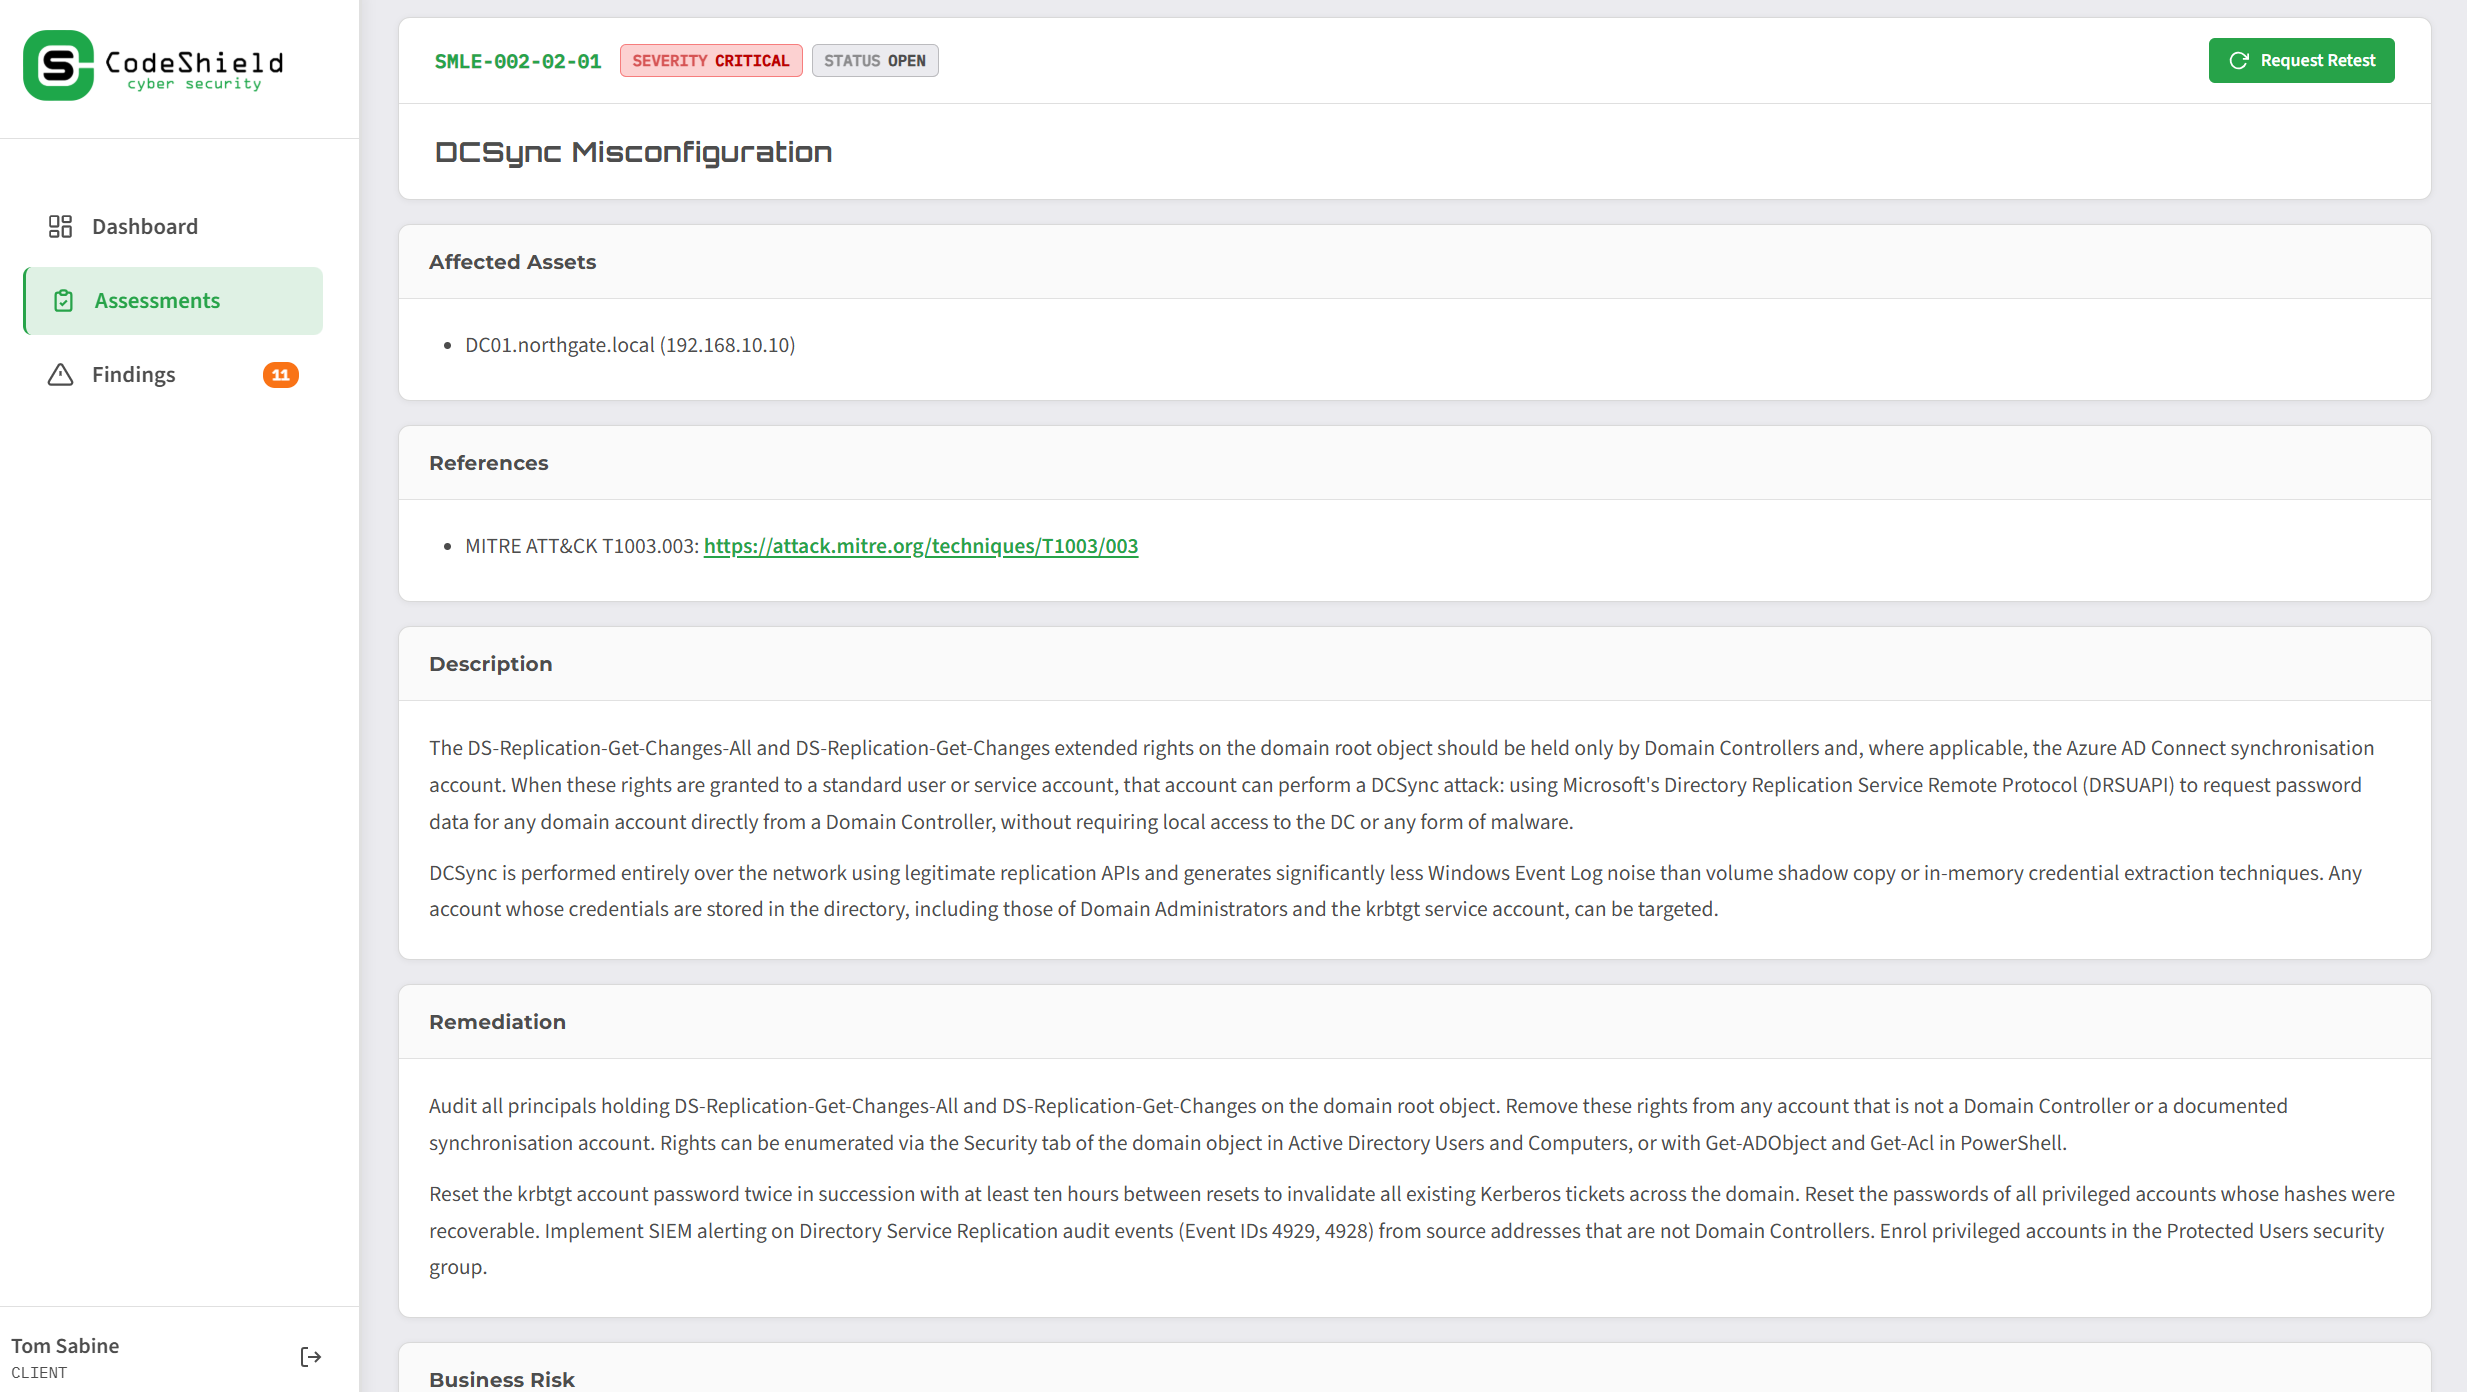
Stay informed throughout your penetration test with real-time access to findings through our secure client portal.
As vulnerabilities are identified, they’re immediately available for your team to review, giving you complete visibility into the assessment as it progresses. Any High or Critical findings are communicated straight away via your agreed contact channels, ensuring urgent risks are never left waiting until the final report.
Our collaborative approach also allows for interactive re-testing during the engagement. As fixes are implemented, our consultants can validate them in real time, helping to reduce outstanding vulnerabilities before testing is complete.
At the end of the engagement, your portal is updated with the final quality-assured report, providing a comprehensive record of the assessment, findings, remediation guidance, and supporting evidence.
TRUSTED UK PENETRATION TESTERS
Contact CodeShield today to get a quote or work with us
At CodeShield, our UK penetration testing team brings 20+ years of combined expertise delivering practical, results-driven security solutions tailored to your business. We offer penetration testing services in Newcastle, so work with us today, as we’re backed by over 12+ 5 star reviews.
Penetration testing Newcastle FAQs
A vulnerability scan is automated and flags known issues. A penetration test adds expert human analysis, actively exploiting weaknesses to understand the real business impact and uncovering the business-logic and chained vulnerabilities that scanners simply cannot find.
Both. A secure model in an insecure application is still a risk, and vice versa. We assess the model’s behaviour, the application logic, the data pipelines, any connected tools or agents, and the supporting infrastructure, giving you a complete picture.
Industry best practice is to test at least annually, and after any significant change to your infrastructure. Frameworks such as PCI DSS and ISO 27001 typically require annual testing. We’ll help you define the right cadence for your organisation.
Yes. Our support doesn’t end at the report. Once you’ve addressed the findings, we can retest to confirm the fixes are effective, giving you and your stakeholders verified assurance that the risks have been closed.
Cloud providers secure the underlying infrastructure, but securing how you configure and use their services is your responsibility. Our testing focuses squarely on that customer side, where the vast majority of cloud breaches actually occur.
Every engagement ends with a comprehensive report detailing the vulnerabilities we found, how they could be exploited, and their potential business impact. Each finding is prioritised by risk and paired with practical, actionable remediation advice, written to be clear for technical teams and senior stakeholders alike.
ISO 42001 is the international standard for AI management systems, and independent security testing helps evidence the controls it expects. Our testing and reporting map findings to relevant requirements, supporting your path to certification and demonstrating responsible AI governance.
