



CREST-accredited penetration testing Services
SOC 2 Penetration Testing
CodeShield delivers CREST-accredited SOC 2 penetration testing that stands up to your auditor’s scrutiny. Whether you are preparing for your first SOC 2 Type I, evidencing controls across a Type II observation window, or renewing an annual report, we give you the independent testing your auditor expects, in a document your CPA firm and your customers can actually use.
No generic checklists. No false positives. Just clear, credible results from a dedicated expert who guides you from scoping through to remediation, and maps every finding back to the Trust Services Criteria your report depends on.

Does SOC 2 actually require a penetration test?
It is the first question almost everyone asks, and the honest answer has some nuance to it.
SOC 2 does not hand you a checklist that names “penetration testing” as a mandatory item. It is an attestation built on the AICPA’s Trust Services Criteria, and your auditor uses judgement rather than a fixed tick-list. What the criteria do expect is that you run ongoing evaluations of your controls and actively identify vulnerabilities in your systems. In practice, penetration testing is the accepted way to evidence that, and most CPA firms and enterprise customers expect to see it.
Put simply: you may pass without a pen test, but very few SaaS businesses do, and testing is one of the fastest ways to give your auditor the evidence they are looking for. If your auditor, or a customer’s security review, expects independent testing, we make satisfying that expectation straightforward.
Not sure where testing fits into your SOC 2 readiness? Talk it through with a tester on a 15-minute scoping call.
START HERE
Which penetration test do you need for SOC 2?
SOC 2 is scoped around the systems that deliver your service, so the right test depends on your architecture. Most SaaS businesses need one or two of the following, and we will help you scope the right combination on a short call. We regularly combine testing types, for example web application plus cloud testing, to cover a platform’s full attack surface in a single engagement.
WHY TRUST CODESHIELD
Trusted & Independently verified.

SOC 2 penetration testing for SaaS and security-conscious businesses
Most organisations pursuing SOC 2 are software businesses whose enterprise customers, often in the US, will not sign without it. We deliver SOC 2 penetration testing across:
Software and data-driven businesses
- B2B SaaS and software platforms: the core use case. Testing the product your enterprise customers are running their own security reviews against.
- FinTech and Financial Services: evidencing security for SOC 2 alongside FCA and PCI DSS expectations, protecting payment flows and customer accounts.
- Health Tech: securing patient and health data for SOC 2 while aligning with wider healthcare requirements.
- HR and Payroll Software: protecting some of the most sensitive personal data any system holds.
- Data and Analytics providers: testing the platforms that process high-value customer data.
Growing businesses selling into enterprise
- Professional Services and Managed Services: protecting client data across distributed teams and remote access.
- Insurance and InsurTech: testing the platforms that hold high-value personal and claims data.
If you are a UK or European business being asked for a SOC 2 report by US enterprise buyers, or you are building SOC 2 into your growth plan, our penetration testing is built for you.

WHY CODESHIELD – 20+ YEARS EXPERIENCE
You work with the person doing the testing.
At CodeShield, our UK penetration testing team brings 20+ years of combined expertise delivering practical, results-driven security solutions tailored to your business.
You work directly with a fully-qualified pen tester. You meet them before you pay, so you know who you’re working with.

Our Values
What’s in your penetration testing report
The report is where a penetration test earns its value. A test is only as useful as the document that comes out of it, and ours are built to be read and acted on, not filed away. Every engagement ends with a clear, structured report that works for your technical team and your senior stakeholders alike.
See a sample report
Want to see the quality of our reporting before you commit? Download an anonymised sample penetration testing report and see exactly what you’ll receive: the structure, the depth of detail, and the clarity of our remediation advice.

Meet your SOC 2 requirements with confidence
Many organisations first come to us because a CPA firm, or an enterprise customer’s security team, requires independent penetration testing as part of SOC 2. We make that requirement straightforward to satisfy, and turn a tick-box exercise into genuine security improvement.
Our testing also supports the other frameworks you are likely juggling alongside SOC 2:
- ISO 27001: independent testing to evidence your information security controls.
- PCI DSS: testing to meet cardholder data security obligations.
- Cyber Essentials Plus: hands-on assessment beyond the self-certified baseline.
- NHS DSP Toolkit: testing aligned to data security standards for health and care organisations.
- FCA and Financial Services requirements: supporting the security expectations placed on regulated firms.
You will receive a clear, audit-ready report that maps findings to the Trust Services Criteria your auditor is assessing, with practical remediation advice to close the gaps, not just document them.
LIVE REPORTING
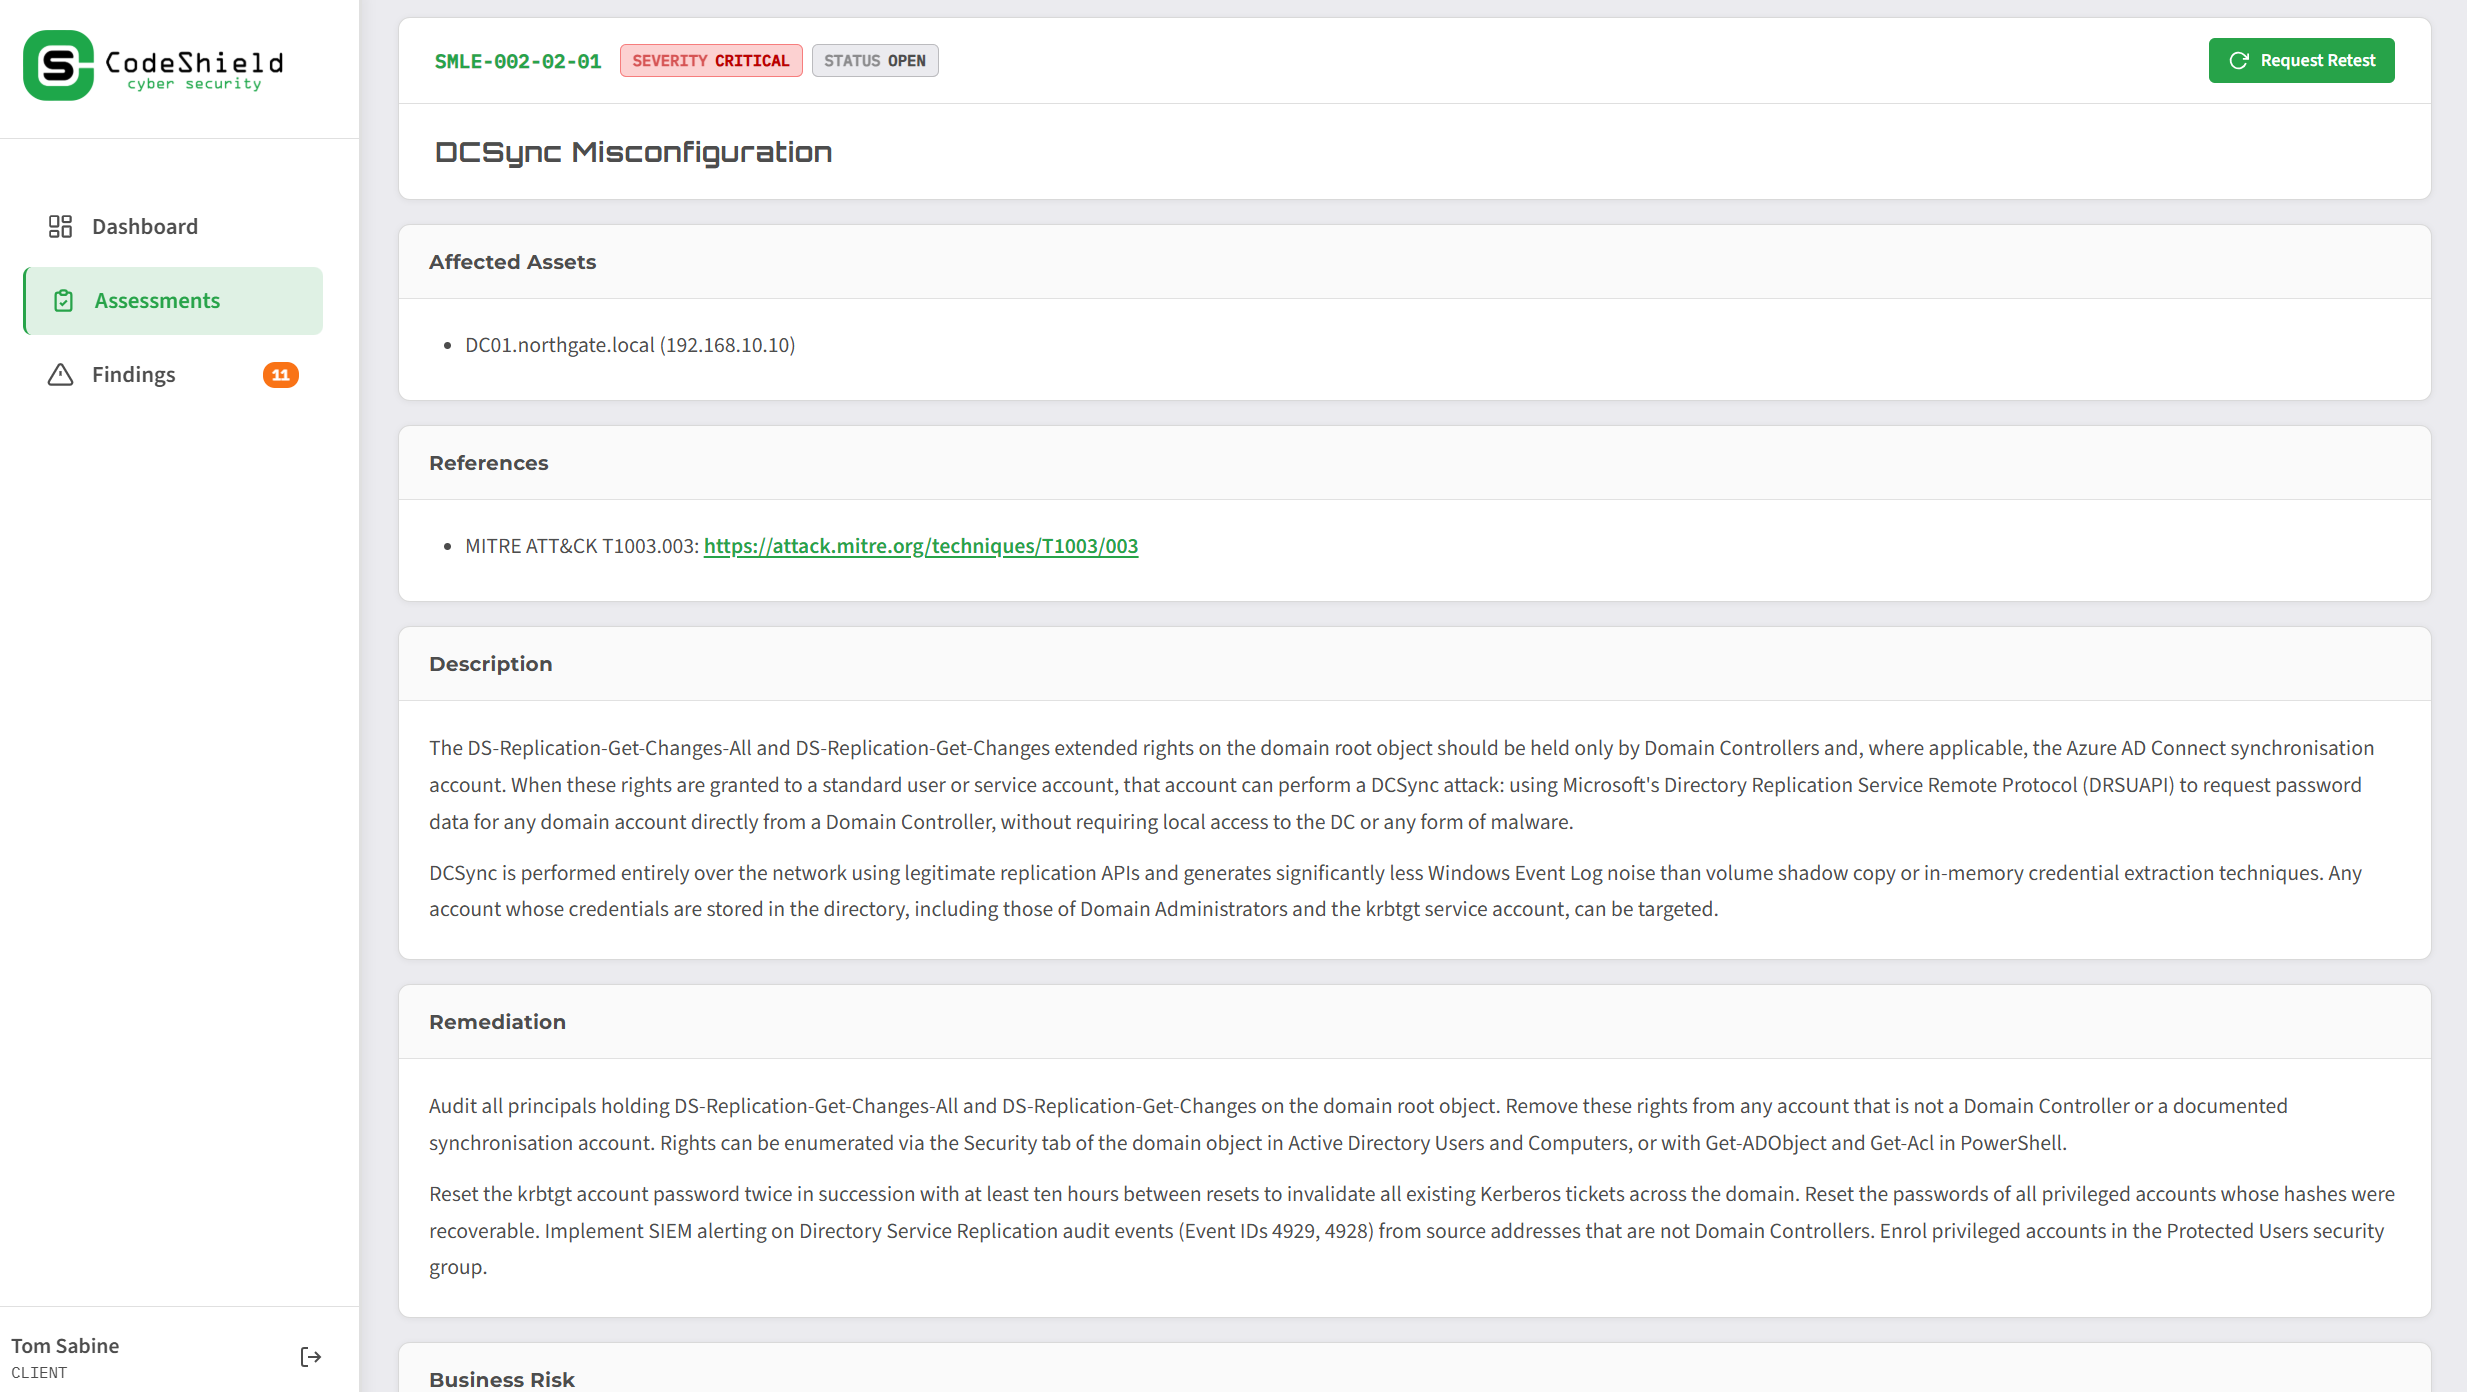
Stay informed throughout your penetration test with real-time access to findings through our secure client portal.
Stay informed throughout your SOC 2 penetration test with real-time access to findings through our secure client portal.
As vulnerabilities are identified, they are immediately available for your team to review, giving you complete visibility as the assessment progresses. Any High or Critical findings are communicated straight away via your agreed contact channels, so urgent risks are never left waiting until the final report.
Our collaborative approach also allows for interactive re-testing during the engagement. As fixes are implemented, our consultants validate them in real time, helping you reduce outstanding vulnerabilities, and close findings, before your audit window closes. At the end of the engagement, your portal is updated with the final quality-assured report: a comprehensive, audit-ready record of the assessment, findings, remediation guidance and supporting evidence.
TRUSTED UK PENETRATION TESTERS
Contact CodeShield today to get your SOC 2 pen test quote
At CodeShield, our UK penetration testing team brings 20+ years of combined expertise delivering practical, results-driven security tailored to your business.
Penetration testing FAQs
Wherever possible we test in a staging or non-production environment to avoid any disruption. If production testing is necessary, we agree all precautions with you during scoping to keep your application stable throughout.
Most major providers now permit customer-authorised penetration testing of your own environment, though some activities carry specific rules. We handle this as part of scoping, ensuring all testing stays within your provider’s acceptable use policies.
No. Wherever possible we test against a non-production environment such as UAT or QA, so there’s no risk to your live service. If that isn’t possible, we take a more cautious approach to post-exploitation testing to protect your users.
Industry best practice is to test at least annually, and after any significant change to your infrastructure or applications. Frameworks such as PCI DSS and ISO 27001 typically require annual testing. We’ll help you define the right cadence for your organisation.
Yes. APIs are one of the most common sources of serious vulnerabilities, so every connected endpoint receives the same scrutiny as the application itself, including tests for authentication gaps, excessive data exposure, and broken object-level authorisation.
Traditional testing simulates attacks against applications and infrastructure. Cloud penetration testing goes deeper into cloud-specific concerns, reviewing IAM policies, storage configurations, and platform settings within AWS, Azure, and Google Cloud to reduce the risk of a breach caused by misconfiguration.
A vulnerability scan is automated and flags known issues. A penetration test adds expert human analysis, actively exploiting weaknesses to understand the real business impact and uncovering the misconfigurations, credential issues, and lateral movement paths that scanners simply cannot find.
Yes. Our support doesn’t end at the report. Once you’ve addressed the findings, we can retest to confirm the fixes are effective, giving you and your stakeholders verified assurance that the risks have been closed.
